Cybersecurity Compliance Services: A Complete Guide
Organizations across Australia, New Zealand, the United States, and Dubai face mounting pressure to demonstrate cybersecurity compliance. Regulatory frameworks continue to expand, auditors demand evidence of control effectiveness, and customers expect proof of security maturity. For businesses without dedicated internal security teams, navigating these requirements often feels overwhelming. Cybersecurity compliance services provide the expertise, structure, and ongoing support needed to meet obligations while building genuine resilience against threats. This guide explains what these services deliver, how they work, and what decision-makers should consider when evaluating providers.
What Cybersecurity Compliance Services Include
Cybersecurity compliance services encompass the full lifecycle of meeting regulatory, industry, and contractual security obligations. These services begin with understanding which frameworks apply to your organization and extend through implementation, validation, and continuous monitoring.
Core Components of Compliance Programs
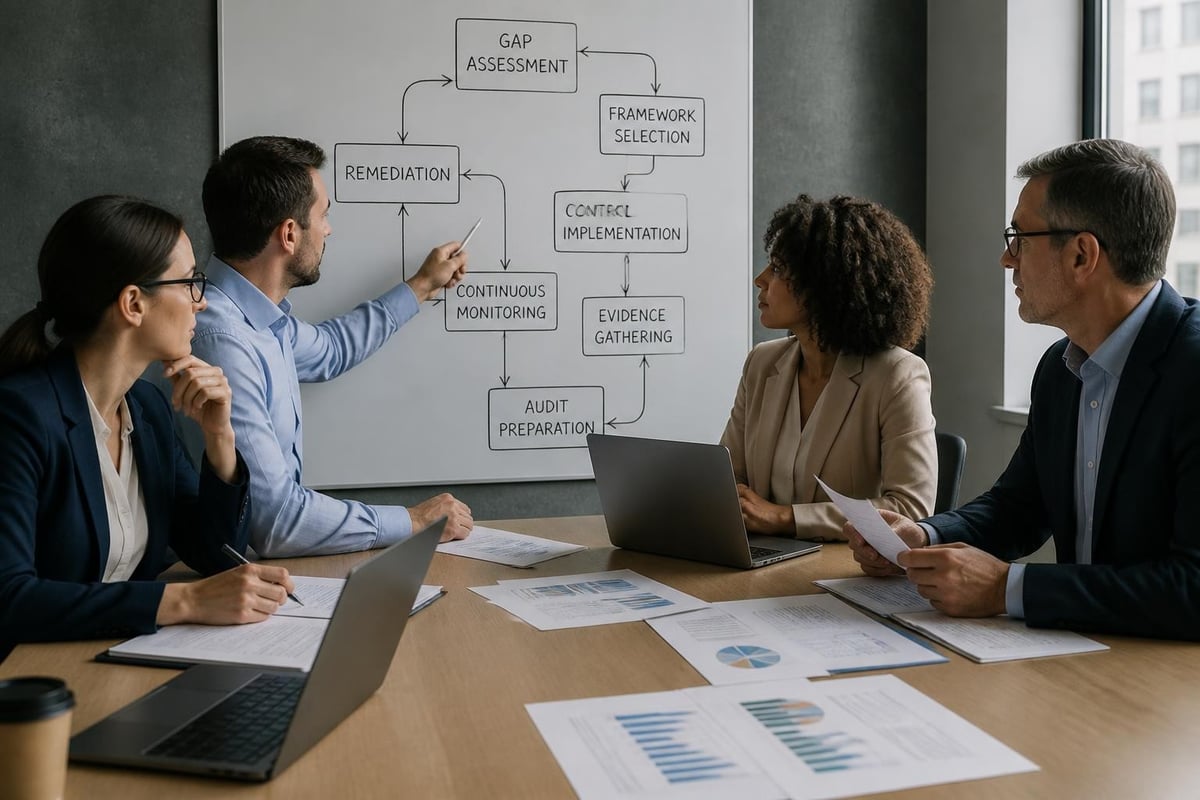
A comprehensive compliance engagement typically includes several distinct workstreams:
- Gap assessment to identify current state versus required controls
- Framework mapping to align your operations with specific standards
- Policy and procedure development tailored to your business context
- Control implementation with technical and administrative safeguards
- Evidence collection systems for audit readiness
- Staff training to embed security awareness across the organization
- Ongoing monitoring to track control effectiveness and regulatory changes
The right combination depends on your industry, geography, existing security posture, and specific obligations. A payment processor in the US will prioritize different frameworks than a healthcare provider in Australia or a SaaS vendor serving European customers.
Framework Selection and Multi-Framework Management
Many organizations must satisfy multiple frameworks simultaneously. The CIS Critical Security Controls provide a prioritized baseline that maps well to numerous regulatory requirements, making them a practical starting point for businesses building their first formal program.
| Framework | Primary Focus | Common Industries |
|---|---|---|
| ISO 27001 | Information security management | Technology, finance, professional services |
| PCI DSS | Payment card data protection | Retail, e-commerce, hospitality |
| GDPR | Personal data privacy | Any organization processing EU resident data |
| SOC 2 | Service organization controls | SaaS, cloud providers, managed services |
| HIPAA | Protected health information | Healthcare, medical billing, health tech |
Professional cybersecurity compliance services help organizations identify overlapping requirements and build unified control sets that satisfy multiple obligations efficiently. This approach reduces duplication, lowers costs, and creates a more maintainable security program.
How Compliance Services Differ from DIY Approaches
Decision-makers often ask whether compliance can be handled internally versus engaging specialized services. The answer depends on several factors, but the differences in outcomes are significant.
Expertise and Certification Requirements
Compliance frameworks require interpretation. Standards like ISO 27001 are deliberately flexible to accommodate different organizational contexts, but this flexibility creates implementation challenges. Experienced practitioners understand how auditors interpret requirements, which controls provide genuine risk reduction versus checkbox compliance, and how to structure evidence for efficient validation.
Many frameworks also require specific certifications or accreditations. ISO 27001 implementation partners should hold relevant qualifications such as ISO/IEC 27001 Lead Implementer credentials. Penetration testers should demonstrate professional certifications like CREST or OSCP. Managed VAPT and Forensics engagements benefit from this specialized expertise, particularly when scope extends beyond simple vulnerability scanning to include business-contextualized testing.
Time-to-compliance represents another critical difference. Internal teams learning frameworks while handling their primary responsibilities often take 18-24 months to reach audit readiness. Specialist providers leveraging established methodologies and templates typically compress this timeline to 6-12 months.
Ongoing Maintenance and Monitoring
Compliance is not a one-time project. Regulations evolve, new threats emerge, business operations change, and controls drift over time. Effective cybersecurity compliance services include mechanisms for continuous monitoring, periodic reassessment, and adaptation to changing requirements.
The NIST Cybersecurity Framework 2.0 emphasizes governance and continuous improvement as core functions, reflecting this reality. Organizations that treat compliance as a project rather than a program inevitably face gaps when audit cycles return or regulations change.
Key Services Within Comprehensive Compliance Programs
Understanding specific service categories helps decision-makers identify what their organization needs now versus what can be phased in over time.
Governance, Risk, and Compliance (GRC) Strategy
GRC services establish the foundation for all compliance activities. This includes defining governance structures, clarifying roles and accountability, establishing risk tolerance, and selecting appropriate frameworks. Without this foundation, compliance efforts become fragmented and difficult to sustain.
Businesses can explore how governance frameworks and GRC strategy services align security activities with business objectives while meeting regulatory requirements.
Risk Assessment and Treatment
Every major compliance framework requires documented risk management. This involves identifying information assets, assessing threats and vulnerabilities, evaluating impact and likelihood, and implementing risk treatment plans.
Risk assessments should be tailored to your business model, not generic templates. A logistics company faces different risks than a financial services firm, even when both pursue ISO 27001 certification.
Policy, Standards, and Procedures
Compliance frameworks require documented security policies. These must reflect actual organizational practices, not aspirational statements copied from templates. Effective policies are:
- Clear and actionable with defined responsibilities
- Aligned with business operations and practical to implement
- Regularly reviewed and updated as the business evolves
- Communicated effectively to all relevant personnel
Many organizations underestimate the effort required to develop, approve, and maintain policy frameworks. Professional services accelerate this process while ensuring policies meet auditor expectations.
Technical Control Implementation
Documentation alone does not satisfy compliance requirements. Organizations must implement and maintain technical controls including access management, network segmentation, encryption, logging and monitoring, vulnerability management, and incident response capabilities.
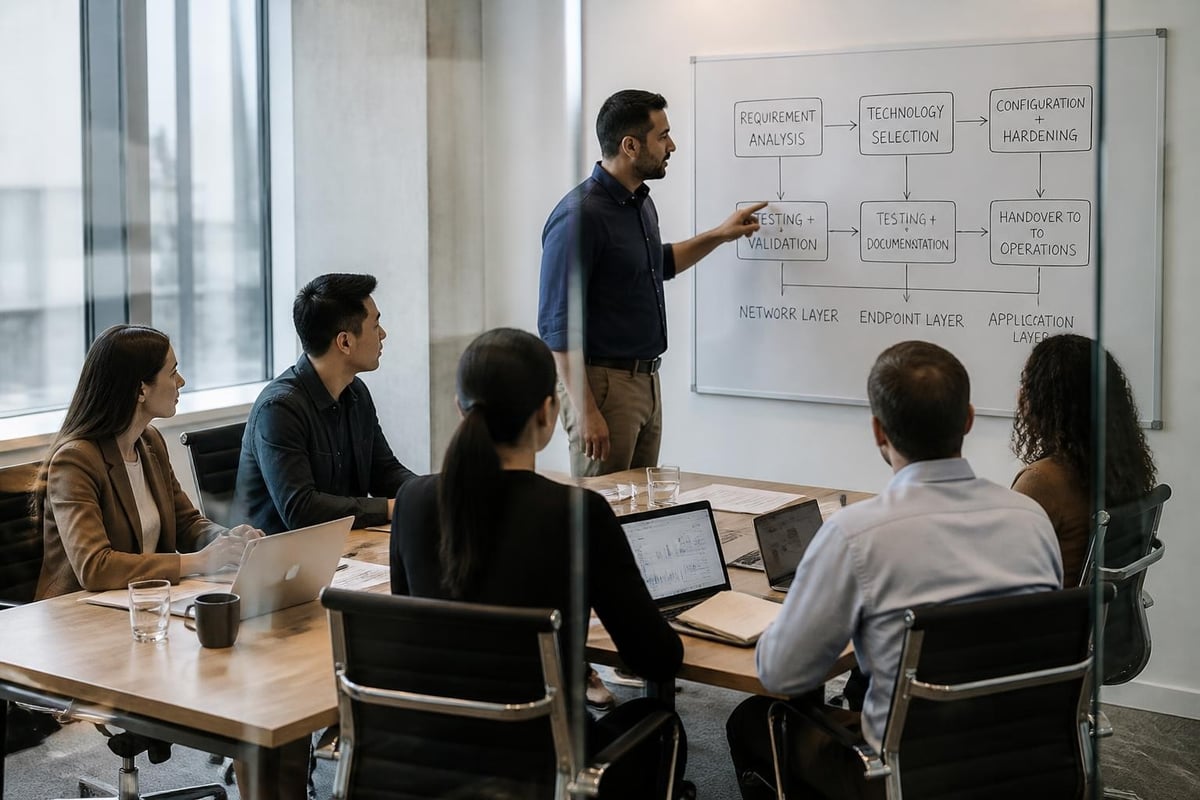
For businesses without internal security infrastructure, managed services provide these capabilities without requiring capital investment in tools or hiring specialized personnel. The key is ensuring controls are scoped appropriately to your actual risk profile and compliance obligations.
Audit Preparation and Evidence Management
Compliance validation requires presenting evidence to external auditors or assessors. This evidence must demonstrate that controls are designed appropriately, implemented as described, and operating effectively over time.
Organizations often struggle with evidence collection, particularly continuous evidence like access logs, change records, and security monitoring data. Cybersecurity compliance services include systems for ongoing evidence capture, organization, and presentation in audit-ready formats.
The AICPA Trust Services Criteria provide detailed guidance on the types of evidence auditors expect for SOC 2 engagements, offering insight into general audit preparation approaches.
Choosing the Right Compliance Service Provider
Not all cybersecurity compliance services deliver the same value. Decision-makers should evaluate providers across several dimensions to ensure alignment with their organization's needs.
Provider Qualifications and Experience
Verify that providers hold relevant professional certifications and have demonstrable experience with your specific frameworks and industry. Request references from similar organizations and ask detailed questions about their implementation methodology.
Warning signs include providers who:
- Promise unrealistic timelines or guaranteed certification outcomes
- Rely heavily on generic templates without customization
- Cannot explain their approach to handling framework updates
- Lack staff with relevant professional credentials
- Focus exclusively on documentation without addressing technical controls
Service Delivery Models
Compliance services are delivered through various models, each with different implications for cost, control, and long-term capability building.
| Model | Description | Best For |
|---|---|---|
| Project-based | Fixed-scope engagement to achieve specific milestone | Initial implementation, certification preparation |
| Retained advisory | Ongoing monthly engagement for guidance and review | Organizations with internal teams needing expert oversight |
| Fully managed | Provider handles all compliance activities | Businesses without security staff or expertise |
| Hybrid | Combination of project, retained, and managed elements | Growing organizations transitioning to internal capability |
Many businesses begin with project-based implementation services, then transition to retained advisory or managed models for ongoing maintenance. This phased approach balances cost, capability development, and risk.
Technology and Methodology Transparency
Effective compliance services leverage proven methodologies and, where appropriate, technology platforms for evidence collection, risk tracking, and control monitoring. Providers should clearly explain their approach, what tools they use, and how you retain access to your compliance data if the relationship ends.
Avoid providers who lock compliance information in proprietary systems without clear data portability. Your compliance evidence and documentation should remain accessible and under your control.
Implementation Process and Timeline Expectations
Understanding how cybersecurity compliance services are delivered helps set realistic expectations and plan internal resource allocation.
Typical Implementation Phases
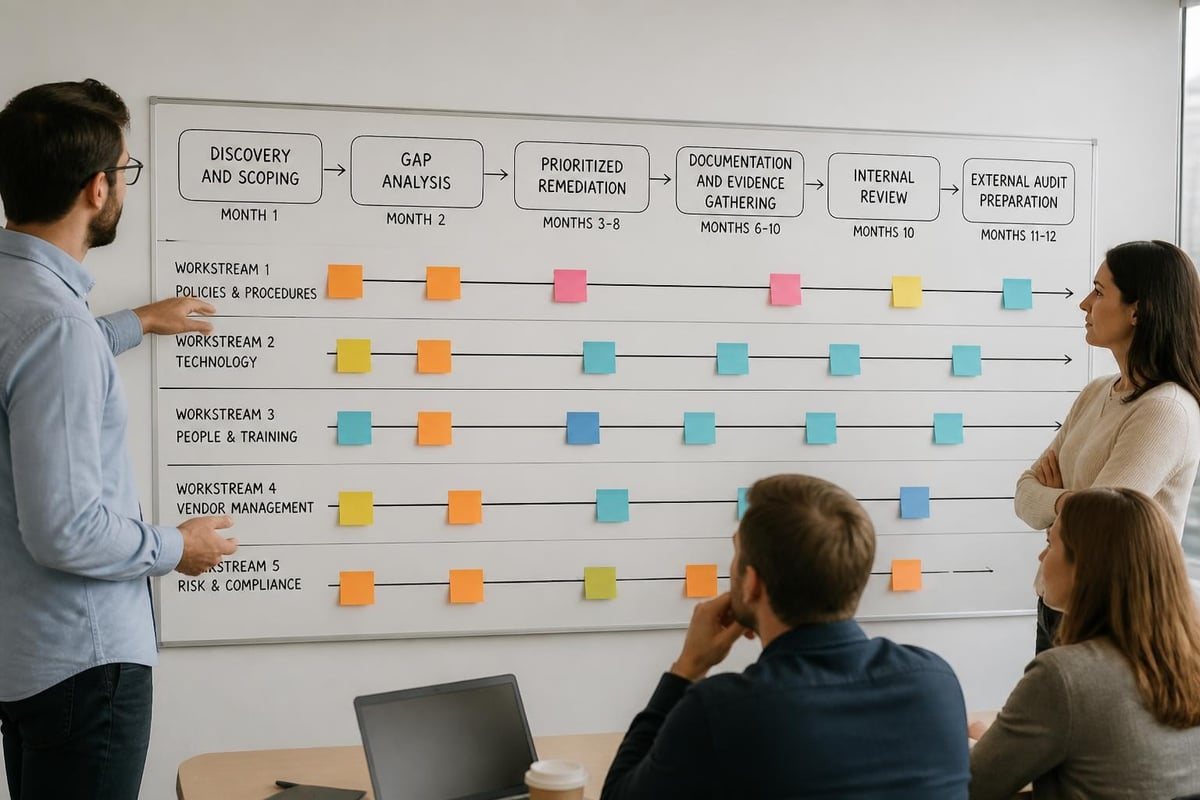
Most compliance implementations follow a structured progression:
- Discovery and scoping to understand current state, define objectives, and establish boundaries
- Gap analysis comparing current controls against framework requirements
- Remediation planning prioritizing gaps based on risk and audit timeline
- Control implementation deploying technical and administrative safeguards
- Documentation and evidence collection building the audit package
- Internal review validating readiness before external assessment
- External audit or certification formal validation by independent assessor
Timeline varies significantly based on framework complexity, organizational size, and starting maturity. ISO 27001 implementations typically require 6-12 months. PCI DSS compliance for a straightforward e-commerce environment might take 3-6 months. Multi-framework programs spanning ISO 27001, SOC 2, and GDPR often extend to 12-18 months.
Internal Resource Requirements
Even when engaging external cybersecurity compliance services, organizations must allocate internal resources. Executive sponsorship ensures the program receives appropriate priority and resources. A compliance project lead or steering committee provides decision-making and coordination. Subject matter experts from IT, HR, legal, and operations supply business context and implement controls within their domains.
Businesses should budget approximately 10-20% of total project time for internal participation, varying by engagement model and organizational complexity.
Cost Considerations and Budgeting
Compliance investments span service fees, technology, internal time, and audit or certification costs. Understanding these components helps decision-makers build realistic budgets.
Service Fee Structures
Providers structure fees differently based on delivery model:
- Fixed-price projects for defined scope implementations
- Time-and-materials for exploratory or evolving engagements
- Monthly retainers for ongoing advisory or managed services
- Per-control or per-requirement pricing less common but used by some providers
Request detailed proposals that itemize services, deliverables, assumptions, and exclusions. Understand what happens when scope expands or timeline extends.
Technology and Tool Costs
Compliance often requires security tools for access control, monitoring, vulnerability management, and evidence collection. Some providers include these in service fees, while others treat them as separate line items or expect clients to procure directly.
Clarify ownership, licensing terms, and ongoing costs for any technology components. Managed service models typically bundle technology access into monthly fees, simplifying budgeting but creating long-term commitments.
Certification and Audit Fees
External validation carries separate costs paid directly to certification bodies or audit firms. ISO 27001 certification audits typically range from $15,000 to $50,000 depending on organizational scope and complexity. SOC 2 audits range from $20,000 to $100,000+ based on system boundaries and control objectives. PCI DSS validation costs vary dramatically based on merchant level and assessment method required.
These fees recur annually or periodically for surveillance audits and recertification, representing ongoing compliance program costs beyond initial implementation.
Regulatory Landscape and Framework Updates
The compliance landscape evolves constantly. New regulations emerge, existing frameworks receive updates, and enforcement priorities shift. Professional cybersecurity compliance services monitor these changes and help organizations adapt.
Recent Framework Evolution
The NIST Cybersecurity Framework updated to version 2.0 in 2024, adding Govern as a sixth core function and emphasizing supply chain security and governance integration. Organizations using CSF as their compliance baseline need to update their implementations accordingly.
ISO/IEC 27001 updated to the 2022 edition, introducing new controls around threat intelligence, cloud security, and configuration management. Organizations certified under the 2013 standard must transition by October 2025.
The PCI Security Standards Council released PCI DSS v4.0 with new requirements for multi-factor authentication, password strength, and vulnerability management. Organizations have until March 2025 to implement all new requirements.
Regional Regulatory Developments
The European Union continues expanding cybersecurity requirements through NIS2, the Cyber Resilience Act, and sector-specific regulations. The 2024 ENISA report on cybersecurity in the Union provides comprehensive analysis of these evolving obligations and their implementation timelines.
Australia's Privacy Act review proposes significant changes to data protection requirements, potentially requiring organizations to reassess their compliance programs. The Essential Eight maturity model receives periodic updates reflecting evolved threat landscapes.
Dubai and the broader UAE continue developing their cybersecurity regulatory framework, with industry-specific requirements in financial services, healthcare, and critical infrastructure. Organizations operating across these regions face complex multi-jurisdictional compliance challenges requiring coordinated approaches.
Common Compliance Challenges and Solutions
Organizations pursuing cybersecurity compliance encounter predictable obstacles. Understanding these challenges and proven solutions helps decision-makers avoid common pitfalls.
Scope Creep and Resource Constraints
Compliance projects often expand as teams discover additional systems, data flows, or requirements. Effective scope management requires clear boundaries agreed upfront, formal change control processes, and realistic resource planning that accommodates some expansion.
Professional services help contain scope by establishing clear inclusion/exclusion criteria and managing stakeholder expectations about what the current phase addresses versus future iterations.
Balancing Security and Business Operations
Compliance controls must enhance security without blocking legitimate business activities. This balance requires understanding workflows, consulting users, and designing controls with operational context. Generic implementations often create friction that leads to workarounds undermining both security and compliance.
Organizations implementing ISO 27001:2022 ISMS benefit from structured approaches that embed security into business processes rather than layering it on afterward. This alignment reduces resistance and improves long-term control sustainability.
Maintaining Compliance Over Time
Initial certification is just the beginning. Controls drift as staff change, systems evolve, and business priorities shift. Sustained compliance requires ongoing monitoring, periodic reassessment, and continuous improvement.
Managed compliance services address this challenge through regular control testing, quarterly reviews, and proactive updates when frameworks or business conditions change. For organizations reviewing managed cybersecurity options, integrated compliance monitoring provides significant value beyond standalone security operations.
Demonstrating Value Beyond Checkbox Compliance
Leadership often views compliance as a cost center required to satisfy external obligations. Effective cybersecurity compliance services demonstrate value through risk reduction, incident prevention, operational improvements, and competitive advantage.
Quantifying compliance benefits requires tracking metrics like vulnerability remediation timeframes, incident response capabilities, security awareness improvements, and third-party validation outcomes. These measurements help justify ongoing investment and secure executive support.
Integration with Broader Security Programs
Cybersecurity compliance services deliver maximum value when integrated with comprehensive security strategies rather than operating in isolation.
Compliance-Driven Security Architecture
Compliance requirements provide a useful forcing function for security architecture decisions. Access controls required by SOC 2 improve overall security posture. Vulnerability management mandated by PCI DSS reduces exposure across all systems. Incident response procedures required by GDPR strengthen operational resilience.
Forward-thinking organizations use compliance as an opportunity to build foundational security capabilities that extend beyond minimum regulatory requirements.
Vendor and Third-Party Risk Management
Most compliance frameworks require organizations to manage third-party security risks. This includes vendor due diligence, contract requirements, and ongoing monitoring of suppliers who access your systems or data.
Effective third-party risk programs assess vendors proportionate to their access and criticality, require evidence of their own compliance, and include contractual provisions for security obligations and audit rights.
Incident Response and Breach Notification
Compliance frameworks increasingly require documented incident response capabilities and, in many cases, specific breach notification procedures. European Commission digital privacy guidance details GDPR breach notification obligations, which apply to any organization processing EU resident data regardless of where they are located.
Testing incident response plans through tabletop exercises or simulations helps identify gaps before real incidents occur and demonstrates audit-worthy evidence of preparedness.
Measuring Compliance Program Success
Effective cybersecurity compliance services include mechanisms for measuring program performance and demonstrating continuous improvement.
Key Performance Indicators
Compliance programs should track both leading and lagging indicators:
Lagging indicators (outcome measures):
- Audit findings and observations
- Certification or validation status
- Compliance violations or sanctions
- Incident impact and frequency
Leading indicators (process measures):
- Control implementation percentage
- Policy acknowledgment completion rates
- Training participation and assessment scores
- Vulnerability remediation timeframes
- Evidence collection completeness
Monitoring both types provides early warning of emerging issues while tracking ultimate compliance outcomes.
Continuous Improvement Mechanisms
ISO 27001 and other management system standards require documented continual improvement processes. This includes regular management reviews, corrective action tracking, and periodic reassessment of risk and control effectiveness.
Professional services establish these mechanisms during initial implementation and help organizations maintain them through subsequent cycles. The SANS Institute's guidance on attack surface management offers practical approaches to continuous discovery and assessment that support compliance monitoring.
Cybersecurity compliance services transform regulatory obligations into strategic security advantages when approached comprehensively. The right partner brings specialized expertise, proven methodologies, and ongoing support that extends far beyond initial certification. F&C specializes in managed cybersecurity and compliance, helping organizations across Australia, New Zealand, the US, and Dubai build resilient security programs aligned with business objectives. Whether you are pursuing your first compliance framework or optimizing an existing program, our team is ready to discuss your specific requirements and develop a tailored approach that delivers lasting value. Contact us to explore how we can support your compliance journey.