Information Security Audit Services: Complete Guide 2026
Organizations today face mounting pressure to demonstrate that their information security controls are effective, compliant, and resilient against evolving threats. Information security audit services provide independent, systematic examinations of security posture, control effectiveness, and regulatory alignment. For business leaders in Australia, New Zealand, the United States, and Dubai, these audits offer more than compliance checkboxes-they deliver actionable insights into risk exposure, operational gaps, and strategic security investments.
Whether you are preparing for ISO 27001 certification, validating SOC 2 readiness, or simply seeking assurance that your security program protects critical assets, understanding how information security audit services work is essential. This guide walks through the scope, methodologies, benefits, and practical considerations that inform audit procurement and execution.
What Information Security Audit Services Include
Information security audit services encompass a structured review of an organization's information security controls, policies, processes, and technology implementations. These engagements typically begin with a scoping exercise to define which systems, data, and business functions will be examined.
Scope Definition and Planning
Auditors work with stakeholders to clarify objectives, identify in-scope assets, and align audit criteria with relevant frameworks or regulations. Common frameworks include ISO/IEC 27001, NIST Cybersecurity Framework, CIS Controls, and PCI DSS. The NIST Cybersecurity Framework (CSF) Version 2.0 provides a flexible foundation that many auditors use to map security outcomes across governance, detection, response, and recovery.
Planning also involves determining the audit's depth. Will it be a high-level assessment or a detailed technical examination? For example, a gap assessment might focus on policy documentation and control existence, while a penetration test examines exploitability of vulnerabilities in live systems.
Evidence Collection and Control Testing
Once scope is agreed, auditors collect evidence to validate control design and operating effectiveness. This includes:
- Documentation review: policies, standards, procedures, risk assessments, incident logs
- Interviews: with security teams, IT administrators, business owners, compliance officers
- Technical testing: configuration reviews, vulnerability scans, access control validation, log analysis
- Walkthroughs: observing processes in action to confirm documented procedures match reality
Auditors assess whether controls are appropriately designed to mitigate identified risks and whether they operate consistently. The NIST Guide for Conducting Risk Assessments (SP 800-30) outlines methods for evaluating threats, vulnerabilities, and impacts that inform control selection and audit depth.
Findings, Reporting, and Remediation Support
Audit reports typically categorize findings by severity-critical, high, medium, low-and provide detailed descriptions, evidence, risk impact, and remediation recommendations. Well-structured reports map findings to specific controls or framework requirements, making it easier for internal teams to prioritize and track remediation.
Some information security audit services extend beyond reporting to include remediation planning, control redesign workshops, or follow-up validation audits. This ongoing support transforms audits from point-in-time snapshots into continuous improvement programs.
Types of Information Security Audits
Not all audits serve the same purpose. Understanding the distinctions helps organizations select the right engagement for their objectives.
| Audit Type | Primary Purpose | Common Frameworks | Typical Audience |
|---|---|---|---|
| Compliance Audit | Validate adherence to regulatory or contractual requirements | PCI DSS, HIPAA, GDPR, SOC 2, ISO 27001 | Regulators, customers, certification bodies |
| Internal Audit | Assess control effectiveness and identify improvement opportunities | ISO 27001, NIST CSF, CIS Controls | Management, board, internal assurance |
| Third-Party Audit | Evaluate vendor/supplier security posture | Vendor-specific questionnaires, shared responsibility models | Procurement, risk teams |
| Technical Security Audit | Examine configurations, vulnerabilities, and exploitability | OWASP, CWE, SANS Top 25, vendor benchmarks | Security operations, IT administrators |
Compliance audits are often mandated by industry regulations or customer contracts. For instance, organizations processing credit card transactions must undergo annual PCI DSS assessments by Qualified Security Assessors. The PCI Security Standards Council maintains detailed requirements and assessment procedures for version 4.x and later.
Internal audits, by contrast, are voluntary and management-driven. They support ISO 27001 ISMS Implementation by providing evidence of continual improvement and preparing organizations for external certification audits.
Key Methodologies and Standards
Professional auditors rely on established methodologies to ensure consistency, rigor, and defensibility.
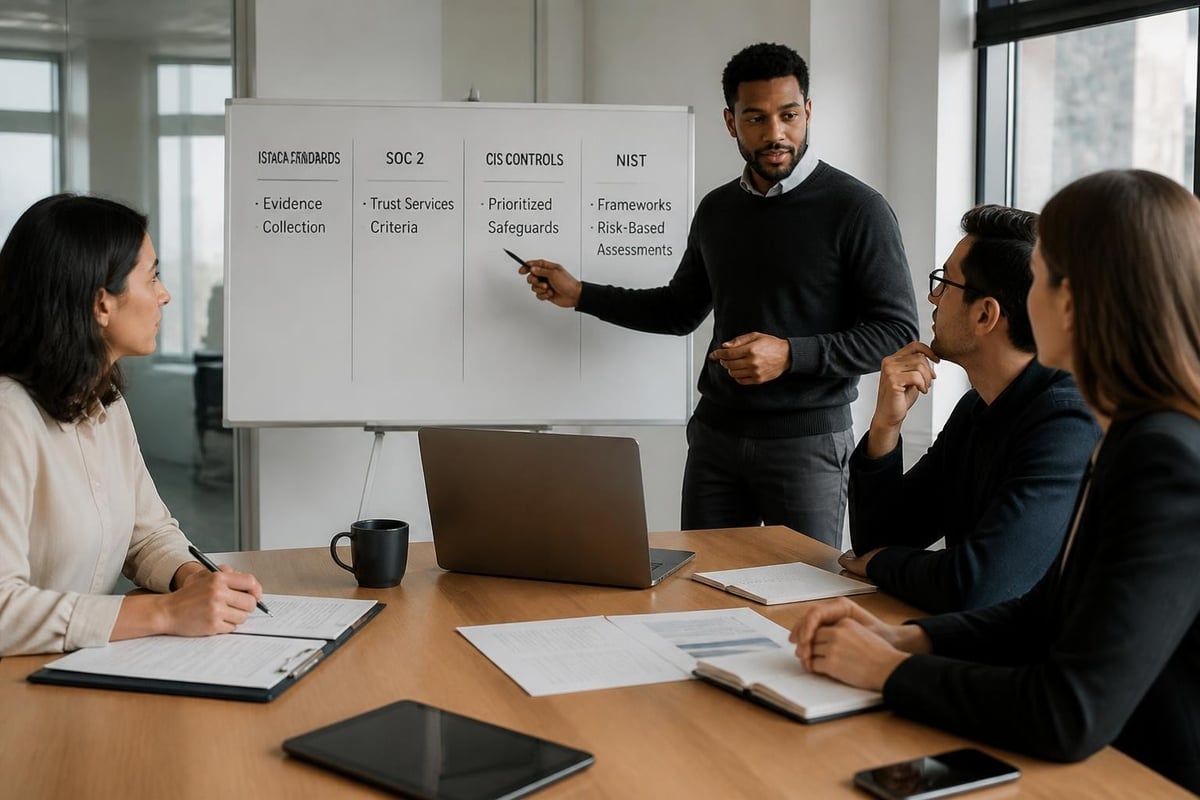
ISACA and Audit Standards
The Information Systems Audit and Control Association (ISACA) publishes frameworks and guidance widely adopted in information security auditing. Their white paper on information systems auditing tools and techniques outlines audit program design, sampling strategies, and evidence documentation practices.
ISACA-certified professionals (CISA, CISM) bring structured approaches to control evaluation, risk prioritization, and stakeholder communication. These certifications signal adherence to internationally recognized audit standards.
SOC Reporting and Attestation
Service Organization Control (SOC) reports are a specialized form of information security audit commonly requested by customers evaluating cloud providers, SaaS platforms, or managed service providers. The AICPA SOC reporting standards define criteria for SOC 1 (financial controls), SOC 2 (security, availability, confidentiality, processing integrity, privacy), and SOC 3 (public-facing summary).
SOC 2 Type II engagements are particularly relevant for technology companies. They require auditors to test control operating effectiveness over a defined period-typically six to twelve months-and issue an attestation report.
Organizations pursuing SOC 2 benefit from aligning their internal controls with Trust Services Criteria before engaging an auditor. This pre-audit alignment reduces findings and accelerates certification.
CIS Controls and Benchmarking
The Center for Internet Security (CIS) Controls provide a prioritized, actionable framework for cyber defense. Version 8.1 organizes 18 controls across Basic, Foundational, and Organizational categories, each with measurable safeguards.
Auditors use CIS Controls Assessment Specification to evaluate implementation maturity and generate scoring metrics. This quantitative approach helps organizations track progress over time and compare performance against industry peers.
Preparing for an Information Security Audit
Preparation significantly influences audit outcomes, timeline, and cost. Organizations that invest in readiness activities reduce findings, streamline evidence collection, and demonstrate a mature security posture.
Document Your Security Program
Auditors expect to see documented policies, standards, procedures, and work instructions that define how security is managed. Key artifacts include:
- Information security policy
- Access control standards
- Incident response procedures
- Risk assessment methodology
- Asset inventory and classification
- Change management records
- Vendor management procedures
Well-maintained documentation accelerates audit fieldwork and provides a foundation for control testing. Organizations struggling with documentation may benefit from policies, standards, and procedures development services to establish a structured governance baseline.
Conduct Pre-Audit Assessments
Gap assessments identify control deficiencies before the formal audit begins. This proactive approach allows time for remediation, reducing the likelihood of critical findings. F&C's gap assessments and remediation services help organizations benchmark current state against target frameworks and build prioritized remediation roadmaps.
Pre-audit vulnerability assessments and penetration tests also reveal technical weaknesses that auditors will likely uncover. Addressing these issues beforehand demonstrates due diligence and control maturity.
Assign Clear Roles and Responsibilities
Audits require coordination across IT, security, compliance, legal, and business units. Designating a single point of contact-often a compliance manager or security officer-streamlines communication and evidence requests.
Internal stakeholders should understand their obligations: providing access to systems, responding to interview questions, and supplying evidence within agreed timelines. Clear role definitions prevent delays and confusion during fieldwork.
Common Audit Findings and How to Address Them
Information security audit services consistently identify recurring control gaps across organizations. Understanding these patterns helps prioritize remediation investments.
Insufficient Access Control Management
Weak access controls-such as excessive user privileges, lack of periodic access reviews, or missing multi-factor authentication-rank among the most common findings. Auditors evaluate whether access is granted based on least privilege, reviewed regularly, and revoked promptly when roles change.
Remediation actions:
- Implement role-based access control (RBAC) aligned to job functions
- Schedule quarterly access reviews with documented approvals
- Enforce multi-factor authentication for privileged accounts and remote access
- Automate deprovisioning workflows tied to HR systems
Incomplete Risk Assessments
Many organizations conduct ad-hoc or outdated risk assessments that fail to inform control selection. Auditors expect risk assessments to identify threats, evaluate vulnerabilities, estimate impacts, and prioritize treatment.
The NIST SP 800-30 risk assessment guide provides a proven methodology. Organizations should document risk treatment decisions and map controls to specific risks, creating traceability for auditors.
Inadequate Patch Management
Unpatched systems expose organizations to known vulnerabilities. Auditors test whether patches are deployed within defined timeframes, whether exceptions are documented and approved, and whether vulnerable systems are isolated pending remediation.
Mature patch management includes:
- Automated vulnerability scanning and asset discovery
- Risk-based prioritization (not just vendor severity ratings)
- Defined timelines for critical, high, medium, and low-severity patches
- Change control integration to manage deployment risks
- Compensating controls for systems that cannot be patched immediately
Gaps in Incident Response Capabilities
Incident response plans often exist on paper but lack testing, defined escalation paths, or integration with detection tools. Auditors assess whether plans address containment, eradication, recovery, and post-incident review.
Tabletop exercises and simulated incidents validate response capabilities and identify process weaknesses. Evidence of regular testing demonstrates operational maturity and supports audit compliance.
Weak Vendor Risk Management
Third-party suppliers introduce risks that many organizations fail to assess systematically. Auditors evaluate whether vendor contracts include security requirements, whether periodic assessments occur, and whether high-risk vendors undergo enhanced due diligence.
Organizations should maintain an inventory of critical vendors, conduct risk-based assessments, and monitor vendor compliance through questionnaires, certifications, or on-site audits. F&C's third-party supplier risk services help establish repeatable vendor assessment programs aligned to business criticality.
Choosing the Right Audit Service Provider
Selecting an audit provider involves evaluating technical expertise, industry experience, certification credentials, and cultural fit.
Look for Relevant Certifications and Accreditations
Professional certifications signal competence and adherence to standards. Key credentials include:
- CISA (Certified Information Systems Auditor)
- CISM (Certified Information Security Manager)
- CISSP (Certified Information Systems Security Professional)
- QSA (Qualified Security Assessor for PCI DSS)
- ISO 27001 Lead Auditor
Accreditation by certification bodies (e.g., UKAS, ANAB, JAS-ANZ) indicates that the provider meets international auditing standards and undergoes regular quality reviews.
Assess Industry and Framework Expertise
Providers with deep experience in your industry understand sector-specific risks, regulatory nuances, and common control challenges. For example, healthcare auditors bring knowledge of HIPAA requirements, while financial services auditors understand PCI DSS and FFIEC expectations.
Framework expertise is equally important. If your objective is ISO 27001 certification, select a provider with a proven track record of successful ISMS implementations and certification readiness engagements. Case studies such as Australia financial software ISMS implementation demonstrate real-world expertise in guiding organizations through certification.
Evaluate Delivery Model and Responsiveness
Some audits are delivered entirely on-site, while others leverage remote evidence collection and virtual interviews. Hybrid models balance efficiency with hands-on testing. Clarify expectations around timelines, deliverables, and communication cadence.
Organizations in Australia, New Zealand, the US, and Dubai should confirm that providers offer responsive support across time zones. While 24/7 response is valuable, it differs from guaranteed response times or continuous SOC monitoring, which are separate service offerings.
Understand Pricing and Scope Management
Audit pricing typically reflects scope complexity, framework requirements, and organization size. Fixed-price engagements provide budget certainty but require precise scoping. Time-and-materials engagements offer flexibility but introduce cost variability.
Request detailed proposals that outline scope, assumptions, exclusions, and deliverables. Clarify whether remediation support, follow-up validation, or ongoing compliance monitoring are included or require separate engagements.
Integrating Audits Into Continuous Improvement
Information security audit services deliver maximum value when integrated into broader governance, risk, and compliance (GRC) programs. Treating audits as isolated events limits their strategic impact.
Establish Audit Cycles Aligned to Business Needs
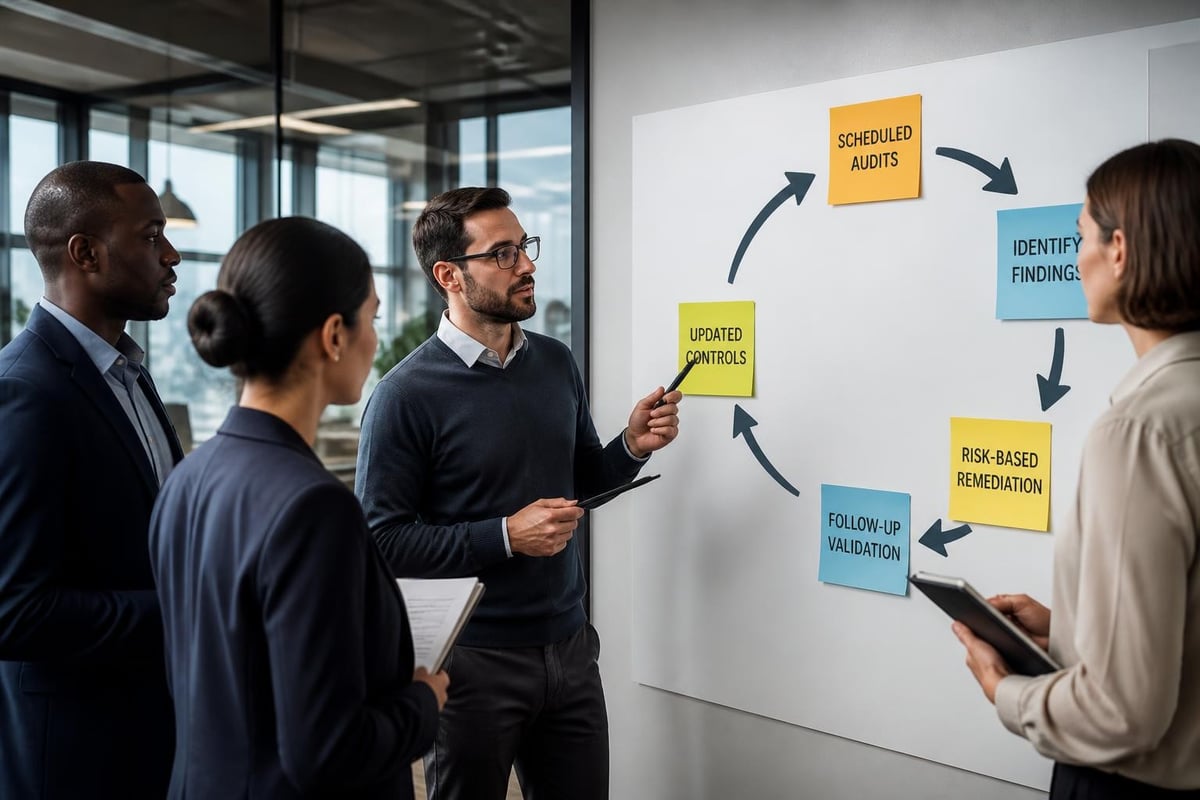
Annual audits support certification maintenance and regulatory compliance. Quarterly or semi-annual internal audits identify emerging risks and validate control improvements. Technical audits (vulnerability assessments, penetration tests) may occur more frequently, especially for high-risk systems or following major changes.
Aligning audit cycles with certification surveillance readiness activities ensures that evidence remains current and controls operate effectively between external assessments.
Use Audit Findings to Drive Risk Treatment
Audit reports should feed directly into risk registers and treatment plans. Each finding represents a control deficiency that increases risk exposure. Prioritize remediation based on risk impact, exploitability, and regulatory consequences.
Track remediation progress using ticketing systems or GRC platforms, assign ownership to specific individuals, and validate closure through follow-up testing. This closed-loop approach transforms findings into measurable security improvements.
Leverage Audit Insights for Board and Executive Reporting
Audit results provide objective, third-party validation of security posture that resonates with boards and executives. Translate technical findings into business language: How does inadequate patch management increase breach likelihood? What financial or reputational impact could result from access control gaps?
Executive dashboards that visualize audit trends-number of findings over time, average time to remediate, percentage of controls operating effectively-demonstrate program maturity and support investment decisions.
Advanced Testing and Specialized Audits
Beyond traditional compliance audits, specialized assessments address emerging risks and technical security domains.
Application Security Audits
Web applications, APIs, and mobile apps introduce unique vulnerabilities. Application security audits examine authentication, authorization, input validation, session management, and data protection controls.
The OWASP Web Security Testing Guide provides comprehensive methodologies for identifying vulnerabilities such as injection flaws, broken access control, and cryptographic failures. These technical audits complement code reviews and static analysis tools.
Organizations developing or operating custom applications should conduct security audits before major releases and periodically during production. Findings inform secure development practices and developer training.
Cloud Security and Configuration Audits
Cloud adoption shifts security responsibilities between providers and customers. Cloud security audits assess whether shared responsibility models are understood, whether configurations follow vendor best practices, and whether data protection controls align to business requirements.
Auditors review identity and access management (IAM), network segmentation, encryption, logging, and backup configurations across infrastructure-as-a-service (IaaS), platform-as-a-service (PaaS), and software-as-a-service (SaaS) environments.
Multi-cloud and hybrid deployments introduce additional complexity. Clear documentation of cloud architectures, data flows, and security controls accelerates audit fieldwork and reduces findings.
Penetration Testing and Red Team Exercises
While traditional audits focus on control existence and design, penetration testing evaluates exploitability. Ethical hackers simulate adversary tactics to identify weaknesses that automated scans miss.
The SANS discussion on continuous penetration testing and offensive SOCs highlights how regular, realistic testing complements formal audits. Penetration tests should follow agreed scope, rules of engagement, and reporting formats that facilitate remediation.
F&C offers Managed VAPT and Forensics services tailored to your business objectives and risk profile. Vulnerability assessment and penetration testing examine weaknesses in authorized systems, while digital forensics helps reconstruct activity when incidents occur.
Regulatory Considerations Across Regions
Organizations operating in multiple jurisdictions must navigate overlapping and sometimes conflicting regulatory requirements.
Australia and New Zealand
The Australian Prudential Regulation Authority (APRA) Prudential Standard CPS 234 mandates information security controls for regulated entities. Privacy regulations under the Privacy Act 1988 and New Zealand Privacy Act 2020 impose data protection obligations that audits often assess.
Essential Eight maturity assessments, aligned to the Australian Cyber Security Centre (ACSC) guidance, are increasingly common in government and critical infrastructure sectors. Auditors evaluate maturity levels across application control, patch management, and other Essential Eight controls.
United States
US organizations face sector-specific regulations: HIPAA for healthcare, GLBA for financial services, FERPA for education, and various state data breach notification laws. Federal contractors must comply with NIST SP 800-171 and CMMC requirements.
The SEC's 2023 cybersecurity disclosure rules require public companies to report material incidents and describe their cybersecurity risk management processes. Audits validate disclosure accuracy and control effectiveness.
Dubai and the Middle East
The UAE's Data Protection Law and Dubai's Data Law establish frameworks for personal data processing. The Dubai Electronic Security Center (DESC) publishes security standards for critical infrastructure and government entities.
Organizations in financial free zones may also face emirate-specific regulations. Auditors familiar with regional requirements ensure that assessments address local compliance obligations alongside international frameworks.
European Union Influence
Although not the primary focus, organizations with EU customers or operations must consider GDPR requirements. The ENISA implementation guidance on security measures provides European perspectives on auditing and assessment schemes, useful for cross-border compliance.
Practical Steps to Initiate an Information Security Audit
For organizations ready to engage information security audit services, follow these steps to ensure a successful outcome.
- Define objectives clearly: Determine whether you need compliance validation, control improvement, certification readiness, or vendor assurance.
- Select the appropriate framework: Align to regulatory requirements, customer expectations, or best-practice standards relevant to your industry.
- Identify in-scope systems and data: Map business processes to information assets, technology platforms, and geographic locations.
- Conduct internal readiness checks: Review documentation, perform gap assessments, and remediate obvious deficiencies.
- Request proposals from qualified providers: Evaluate expertise, certifications, references, and proposed methodology.
- Establish a project team and timeline: Assign roles, schedule fieldwork, and plan for remediation windows.
- Communicate with stakeholders: Prepare employees for interviews, coordinate access, and set expectations around findings.
- Review findings collaboratively: Validate audit evidence, discuss risk ratings, and agree on remediation timelines.
- Implement remediation and track progress: Use structured project management to address findings within target dates.
- Schedule follow-up validation: Confirm that controls operate effectively and findings are fully resolved.
Organizations without dedicated security teams often find value in partnering with managed cybersecurity providers who can prepare for audits, implement remediation, and maintain ongoing compliance. This approach ensures continuity between audit cycles and builds lasting resilience.
Information security audit services transform security posture from aspiration to validated reality, providing the evidence and confidence that stakeholders demand. By selecting the right audit scope, preparing thoroughly, and integrating findings into continuous improvement programs, organizations turn compliance obligations into strategic security investments. F&C helps businesses across Australia, New Zealand, the US, and Dubai navigate the full audit lifecycle-from readiness and gap remediation to certification and ongoing assurance-through our comprehensive cybersecurity and compliance services. Contact us to discuss how we can support your security objectives.