Information Security Systems: A 2026 Buyer's Guide
Information security systems form the foundation of modern business protection, combining people, processes, and technology to safeguard critical assets from evolving threats. For decision-makers without dedicated security teams, understanding what these systems encompass and how they function is essential for making informed investment decisions in 2026. This guide explores the core components, implementation considerations, and strategic value of comprehensive information security systems.
What Information Security Systems Actually Include
Information security systems extend far beyond antivirus software and firewalls. They represent a coordinated ecosystem of policies, controls, technologies, and processes designed to protect confidentiality, integrity, and availability of business information.
Core Components and Layers
Modern information security systems typically incorporate several interconnected elements:
- Access control mechanisms that verify user identity and authorize resource access
- Network security infrastructure including firewalls, intrusion detection, and segmentation
- Endpoint protection covering workstations, mobile devices, and servers
- Data protection measures such as encryption, classification, and loss prevention
- Security monitoring and response capabilities for threat detection and incident handling
- Governance frameworks defining policies, standards, and accountability structures
The CIS Critical Security Controls provide a prescriptive baseline for prioritizing these technical safeguards based on real-world attack patterns.
Technology Versus Management Systems
A critical distinction exists between security technology products and information security management systems (ISMS). Technology tools-firewalls, encryption, scanners-address specific technical risks. An ISMS provides the organizational framework that determines which tools to deploy, how to configure them, who maintains them, and how effectiveness is measured.
Organizations pursuing ISO 27001:2022 ISMS Implementation establish this structured management layer, ensuring security controls align with business objectives and compliance requirements. This systematic approach proves especially valuable for businesses serving regulated industries or handling sensitive customer data.
Building Blocks: Controls and Frameworks
Information security systems rely on documented controls-specific safeguards addressing identified risks. Understanding control categories helps decision-makers evaluate coverage and gaps.
| Control Category | Purpose | Examples |
|---|---|---|
| Preventive | Stop security events before occurrence | Access restrictions, encryption, firewall rules |
| Detective | Identify security events during or after occurrence | Log monitoring, intrusion detection, audit reviews |
| Corrective | Minimize impact and restore normal operations | Incident response, backup restoration, patching |
| Administrative | Establish governance and accountability | Policies, risk assessments, training programs |
Framework Selection Considerations
Multiple frameworks guide information security systems design. Selection depends on regulatory requirements, industry norms, and organizational maturity:
ISO/IEC 27001 offers internationally recognized certification suitable for demonstrating security commitment to customers and partners. The standard requires documented risk assessments, control implementation, and continuous improvement processes.
NIST Cybersecurity Framework provides flexible guidance popular in critical infrastructure sectors and US government contracting. Its five functions-Identify, Protect, Detect, Respond, Recover-structure security programs without prescribing specific controls.
Zero Trust Architecture represents an emerging paradigm assuming breach and requiring continuous verification. Microsoft's Zero Trust guidance provides practical implementation resources for organizations modernizing legacy perimeter-based security models.
The governance frameworks and GRC strategy services offered by specialized providers help businesses select and implement appropriate frameworks aligned with their risk profile and compliance obligations.
Operational Security: Monitoring and Response
Information security systems require active operation, not merely deployment. Continuous monitoring, threat detection, and incident response capabilities distinguish effective programs from checkbox compliance.
Security Operations Center Functions
Whether operated internally, outsourced, or hybrid, SOC capabilities form the operational heart of information security systems:
- Event collection and correlation from network devices, endpoints, applications, and cloud platforms
- Threat intelligence integration to contextualize alerts with current attack trends
- Alert triage and investigation to separate true incidents from false positives
- Incident response coordination to contain threats and minimize business impact
- Vulnerability management to identify and remediate system weaknesses before exploitation
The 2024 SANS SOC Survey identifies staffing challenges and alert fatigue as persistent operational hurdles for security teams managing information security systems.
Threat Intelligence and Attack Mapping
Effective information security systems incorporate threat intelligence to prioritize defenses against likely attack vectors. The MITRE ATT&CK framework catalogs adversary tactics and techniques, enabling organizations to map existing controls against observed threat behaviors and identify coverage gaps.
Understanding current threat landscapes proves essential. The ENISA Threat Landscape 2025 report documents evolving risks including supply chain compromises, ransomware sophistication, and AI-enabled social engineering-all requiring adaptive information security systems responses.
Application and API Security Considerations
As businesses increasingly rely on web applications and API integrations, information security systems must extend protection beyond network perimeters to application layers.
Common Application Security Gaps
Many organizations focus heavily on network security while overlooking application vulnerabilities:
- Broken authentication allowing unauthorized access to user accounts
- Injection flaws enabling attackers to execute malicious commands
- Sensitive data exposure through inadequate encryption or access controls
- Security misconfiguration in frameworks, servers, or cloud platforms
- Insufficient logging that prevents detection of application-layer attacks
The OWASP API Security Top 10 provides authoritative guidance for securing application programming interfaces-increasingly critical as businesses adopt microservices architectures and cloud-native development.
Organizations implementing information security systems should include application security testing as a core component. Regular vulnerability assessment and penetration testing examines weaknesses in authorized systems, helping organizations identify and remediate risks before threat actors exploit them.
Cloud Security and Hybrid Environments
Information security systems in 2026 must address hybrid environments spanning on-premises infrastructure, multiple cloud platforms, and edge computing resources.
Shared Responsibility Model
Cloud security requires understanding the division of responsibilities between cloud service providers and customers:
| Responsibility Area | Infrastructure-as-a-Service | Platform-as-a-Service | Software-as-a-Service |
|---|---|---|---|
| Physical security | Provider | Provider | Provider |
| Network infrastructure | Provider | Provider | Provider |
| Operating system security | Customer | Provider | Provider |
| Application security | Customer | Customer | Provider |
| Data protection | Customer | Customer | Customer |
| Access management | Customer | Customer | Customer |
Google Cloud's security best practices offer practical guidance for implementing information security systems controls in cloud environments, covering identity management, data protection, and operational security.
Multi-Cloud Security Challenges
Organizations using multiple cloud platforms face additional complexity in maintaining consistent information security systems controls. Challenges include:
- Inconsistent identity and access management across platforms
- Varying logging and monitoring capabilities requiring aggregation
- Different encryption and key management approaches
- Diverse compliance attestations and audit requirements
- Multiple security configuration languages and tools
Centralized security orchestration, consistent policy enforcement, and unified visibility become essential for effective multi-cloud information security systems.
Risk Management and Assurance
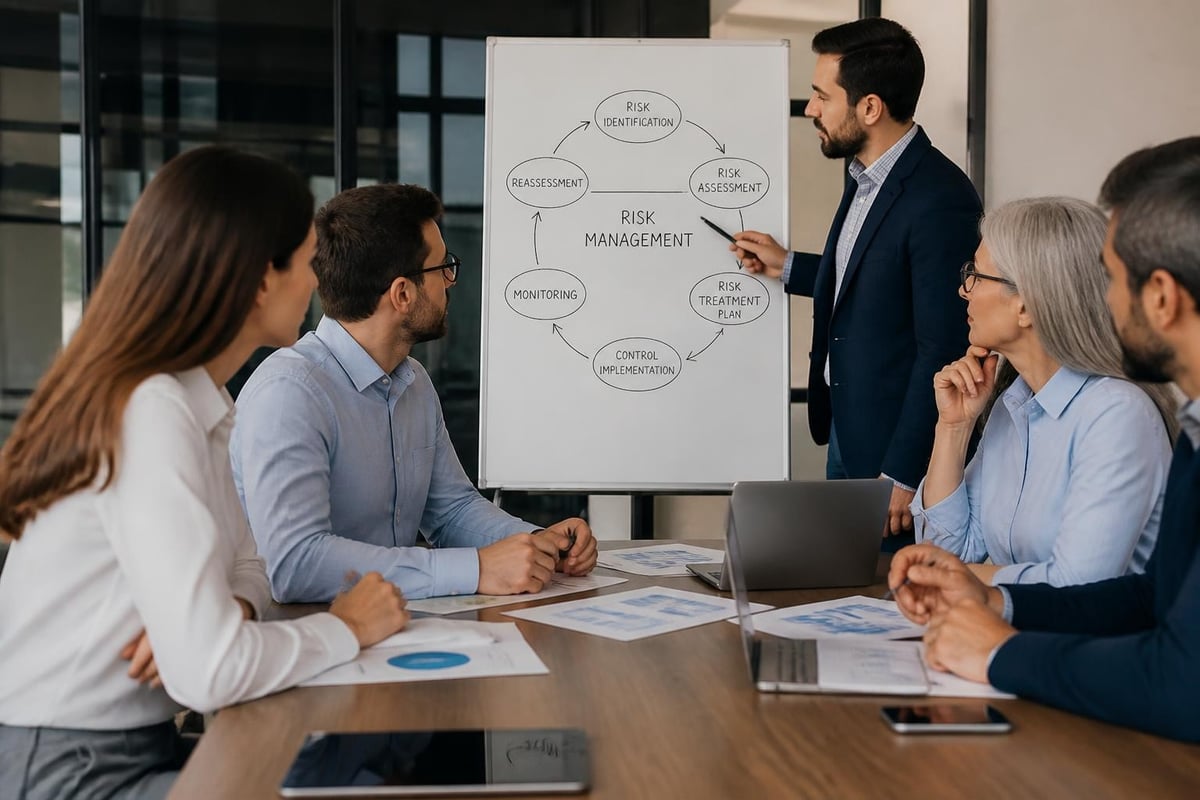
Information security systems exist to manage risk, not eliminate it. Effective programs identify acceptable risk levels, implement proportionate controls, and provide assurance to stakeholders that residual risks remain within tolerance.
Risk Assessment Approaches
Qualitative assessments categorize risks using descriptive scales (high/medium/low) based on likelihood and impact. This approach proves accessible for organizations without extensive security expertise but may lack precision for comparing diverse risk scenarios.
Quantitative assessments estimate risk in monetary terms, calculating potential loss exposure and control cost-effectiveness. While more rigorous, quantitative methods require significant data collection and actuarial expertise.
Most organizations adopt hybrid approaches, using qualitative methods for initial risk identification and quantitative analysis for high-priority risks or investment decisions. Comprehensive information security risk management services help businesses develop appropriate methodologies aligned with their industry and risk appetite.
Assurance and Validation
Information security systems require ongoing validation to confirm controls function as intended. Assurance activities include:
- Internal audits examining control implementation and effectiveness
- External assessments providing independent validation for stakeholders
- Penetration testing simulating real-world attacks against defenses
- Control self-assessments engaging process owners in continuous monitoring
- Third-party certifications demonstrating compliance with recognized standards
A recent systematic literature review explores emerging research in security assurance methods, including AI-enabled approaches to evaluating information security systems effectiveness.
Buying Considerations for Decision-Makers
Organizations evaluating information security systems investments should consider several strategic and practical factors beyond technical specifications.
Build Versus Buy Versus Managed Services
Three primary delivery models exist, each with distinct advantages:
Internal teams provide maximum control and business-specific customization but require significant investment in personnel, training, and technology refresh cycles. This approach suits large organizations with substantial security budgets and complex requirements.
Product licensing offers flexibility in choosing best-of-breed technologies while maintaining operational responsibility internally. Organizations pursue this path when internal expertise exists but specific capabilities require specialized tools.
Managed security services deliver expertise, technology, and operations through external providers. This model benefits organizations without security teams, those requiring 24/7 monitoring capabilities, or businesses seeking to convert capital expenditure to operational expense.
Many successful information security systems combine these approaches-licensing core infrastructure while outsourcing specialized functions like penetration testing, threat intelligence, or incident response.
Evaluating Provider Capabilities
When selecting managed security providers, decision-makers should examine:
- Professional certifications demonstrating practitioner expertise (CISSP, CISM, relevant technology certifications)
- Service delivery approach including response availability, escalation procedures, and reporting cadence
- Technology partnerships indicating deep expertise with specific security platforms
- Compliance experience in relevant regulatory frameworks and industry standards
- Reference customers in similar industries, geographies, and organizational sizes
Organizations should clarify scope boundaries, particularly distinguishing cybersecurity services from general IT support. Understanding whether licensing is included in managed services or purchased separately proves essential for accurate cost comparison.
Integration with Business Processes
Effective information security systems integrate seamlessly with existing business operations rather than creating friction. Evaluation criteria should include:
- Compatibility with current technology investments and cloud platforms
- User experience impact on employees, customers, and partners
- Alignment with change management and release processes
- Scalability to accommodate business growth or seasonal variations
- Reporting capabilities for board-level communication and compliance demonstration
The case studies from security implementations across diverse industries illustrate how information security systems adapt to specific business contexts and operational constraints.
Implementation Roadmap and Maturity
Organizations rarely achieve comprehensive information security systems overnight. A phased approach balances risk reduction with resource constraints and operational disruption.
Maturity Model Stages
Initial/Ad hoc: Security responses remain reactive with inconsistent processes and limited documentation. Controls exist but lack coordination or strategic direction.
Developing: Documented policies and standards emerge with assigned responsibilities. Security practices become repeatable, though not yet optimized or fully integrated with business processes.
Defined: Comprehensive information security systems operate with established governance, regular risk assessments, and integrated controls. Metrics track performance and compliance status.
Managed: Information security systems incorporate continuous improvement with quantitative management. Proactive threat hunting, advanced analytics, and predictive capabilities enhance protection.
Optimizing: Security becomes embedded in organizational culture with innovation, adaptation to emerging threats, and strategic business enablement rather than pure risk mitigation.
Priority Control Implementation
For organizations beginning information security systems development, prioritization proves essential:
- Asset inventory and classification: Understanding what requires protection
- Access control and authentication: Preventing unauthorized access to critical resources
- Patch management: Addressing known vulnerabilities in timely manner
- Data backup and recovery: Ensuring business continuity after security incidents
- Security awareness training: Reducing human-factor risks across workforce
- Incident response planning: Preparing coordinated response to security events
- Network segmentation: Limiting lateral movement opportunities for attackers
- Logging and monitoring: Enabling detection of security events and compliance demonstration
This sequence addresses fundamental risks while building foundations for more sophisticated capabilities. Organizations can tailor prioritization based on specific threat models, regulatory requirements, and business criticality assessments.
Emerging Trends Shaping Information Security Systems
Information security systems continue evolving to address new technologies, changing threat landscapes, and regulatory developments.
Artificial Intelligence Integration
AI technologies create both opportunities and risks for information security systems. AI-enhanced security capabilities include automated threat detection, behavioral analytics, and intelligent response orchestration. AI-specific risks require new safeguards addressing model poisoning, adversarial inputs, and data privacy in machine learning systems.
Organizations deploying AI technologies should evaluate security implications across the lifecycle-from training data protection through model deployment and ongoing monitoring. Specialized providers offer comprehensive approaches connecting protection requirements to application behavior and business decisions.
Privacy and Data Protection Convergence
Information security systems increasingly incorporate privacy requirements as regulations like GDPR, CCPA, and sector-specific data protection laws expand. This convergence requires:
- Privacy by design embedding data protection in system architecture
- Data minimization collecting only necessary information
- Purpose limitation restricting data use to stated purposes
- Individual rights management enabling access, correction, and deletion requests
- Cross-border transfer controls addressing jurisdictional data sovereignty requirements
Supply Chain Security
Third-party dependencies create expanding attack surfaces that information security systems must address. Supply chain security involves:
- Vendor risk assessment and ongoing monitoring
- Software bill of materials (SBOM) for dependency visibility
- Secure development lifecycle requirements for custom applications
- Contractual security obligations and right-to-audit clauses
- Incident notification and breach response coordination
The third-party supplier risk services help organizations extend information security systems governance to partners, contractors, and service providers.
Compliance and Regulatory Alignment
Information security systems increasingly serve dual purposes: protecting business assets and demonstrating compliance with regulatory requirements.
Common Regulatory Frameworks
Different industries and geographies impose varying security obligations:
- Healthcare organizations must satisfy HIPAA (US), Privacy Act (Australia), or equivalent patient data protection requirements
- Financial services face regulations including PCI DSS for payment cards, APRA CPS 234 (Australia), and GDPR (EU/UK)
- Government contractors must meet frameworks like NIST SP 800-171, Essential Eight (Australia), or FedRAMP
- General businesses increasingly face data breach notification laws and baseline security requirements
Information security systems designed for compliance should identify applicable regulations, map controls to specific requirements, maintain evidence of implementation, and demonstrate continuous monitoring. The compliance and regulatory assessment services offered by specialized providers help organizations navigate complex regulatory landscapes.
Certification and Audit Readiness
Pursuing formal certification (ISO 27001, SOC 2, etc.) provides external validation of information security systems and competitive differentiation. Successful certification requires:
- Comprehensive documentation of policies, procedures, and controls
- Evidence collection demonstrating consistent implementation
- Internal audit programs identifying gaps before external assessment
- Management review processes ensuring executive oversight
- Continuous improvement addressing findings and changing risks
Organizations should budget adequate preparation time (typically 6-12 months for initial certification) and ongoing effort for surveillance audits and continuous compliance.
Information security systems represent essential business infrastructure in 2026, protecting assets while enabling digital innovation and stakeholder trust. The most effective implementations combine appropriate technology with structured management processes, continuous monitoring, and alignment to business objectives. For organizations seeking to establish or enhance their security posture, partnering with experienced providers accelerates maturity while avoiding common implementation pitfalls. F&C offers comprehensive managed cybersecurity and compliance services designed to build resilience through understanding your specific risks, implementing proportionate controls, and providing ongoing security partnership backed by professional certifications. Contact our team to discuss your information security systems requirements and explore how we can support your protection objectives.