Network Security and Management: Complete Guide 2026
Modern business operations depend entirely on reliable, secure network infrastructure. As organizations expand their digital footprint across cloud platforms, remote workforces, and interconnected systems, network security and management have become fundamental disciplines that protect business continuity, customer trust, and regulatory compliance. Decision-makers face mounting pressure to balance operational efficiency with increasingly sophisticated cyber threats targeting network perimeters, internal segments, and connected devices.
Understanding Network Security and Management Fundamentals
Network security and management encompasses the policies, technologies, and processes that defend network infrastructure against unauthorized access, misuse, and disruption. This discipline extends beyond traditional firewalls to include segmentation strategies, access controls, monitoring systems, and continuous improvement frameworks that adapt to evolving threats.
Core components include:
- Perimeter defense through next-generation firewalls and intrusion prevention
- Internal segmentation limiting lateral movement
- Identity and access management controlling who reaches what
- Traffic analysis detecting anomalous patterns
- Configuration management ensuring consistent, secure settings
- Incident response protocols activating when defenses are tested
Organizations without dedicated security teams often struggle to maintain visibility across distributed networks. The NIST Cybersecurity Framework (CSF) 2.0 provides a structured approach for business leaders, mapping network security activities to governance, identification, protection, detection, response, and recovery functions. This framework helps decision-makers articulate security requirements without requiring deep technical expertise.
Network Threats Facing Organizations in 2026
Threat actors continually refine their methods, exploiting configuration weaknesses, unpatched vulnerabilities, and human error. According to the ENISA Threat Landscape 2024, ransomware, availability attacks, and supply chain compromises dominate the risk landscape, with network infrastructure serving as the primary battleground.
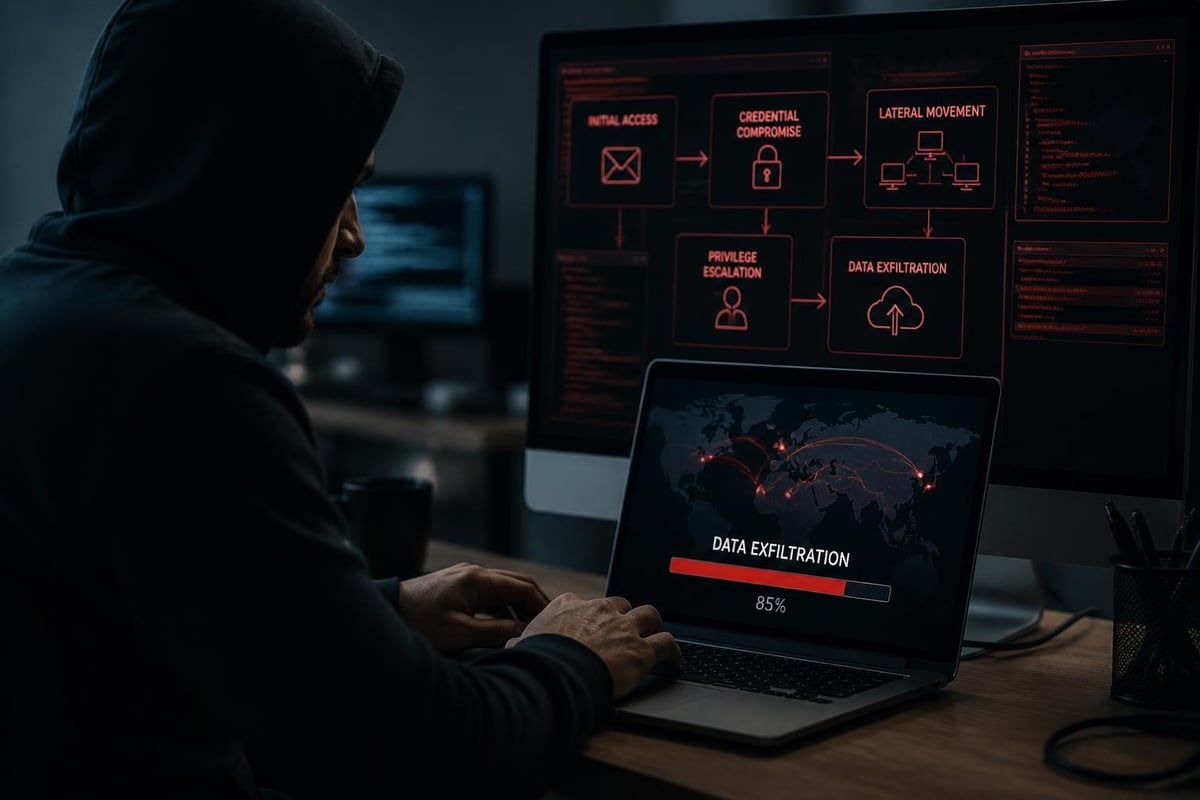
Modern attacks frequently combine multiple vectors. Initial access might occur through compromised credentials or vulnerable network devices, followed by lateral movement across poorly segmented networks, culminating in data exfiltration or encryption. The MITRE ATT&CK Enterprise: Network Devices matrix catalogs specific techniques adversaries use against network infrastructure, providing a threat-informed foundation for defensive planning.
Common network security gaps include:
- Default or weak credentials on network devices
- Insufficient network segmentation allowing unrestricted internal movement
- Outdated firmware creating exploitable vulnerabilities
- Inadequate logging obscuring attacker activity
- Missing encryption exposing data in transit
- Overly permissive firewall rules expanding attack surface
Strategic Framework for Network Security and Management
Effective network security and management requires alignment between business objectives, risk appetite, and technical controls. Organizations should establish baseline security requirements before selecting specific technologies or vendors, ensuring investments address actual risk rather than perceived needs.
Risk-Based Security Planning
Start by identifying critical business systems, data flows, and network dependencies. Map which applications require internet access, which systems communicate internally, and where sensitive data resides. This inventory informs segmentation strategies and control prioritization.
The CIS Critical Security Controls (v8.1) provide prioritized, actionable guidance particularly valuable for organizations building or maturing network security programs. Implementation Groups help decision-makers scale controls to organizational size and complexity, preventing resource waste on premature capabilities.
| Planning Phase | Key Activities | Business Outcome |
|---|---|---|
| Asset Discovery | Inventory network devices, applications, data flows | Visibility foundation |
| Risk Assessment | Identify threats to business-critical systems | Prioritized investment |
| Control Selection | Match controls to risks within budget constraints | Efficient resource allocation |
| Implementation | Deploy, configure, test selected controls | Measurable risk reduction |
| Validation | Verify controls function as intended | Confidence in defenses |
Organizations should document network architecture, security policies, and operational procedures supporting compliance requirements. Structured approaches like ISO 27001 ISMS implementation help businesses systematize network security alongside broader information security management, creating auditable processes that satisfy regulatory expectations.
Network Segmentation and Access Control
Flat network architectures where any device can reach any other device magnify breach impact. Segmentation divides networks into zones based on trust levels, data sensitivity, and functional requirements, containing compromises within limited boundaries.
Effective segmentation strategies:
- Separate production, development, and administrative networks
- Isolate guest wireless from corporate resources
- Create DMZ zones for internet-facing services
- Segment by data classification (public, internal, confidential, restricted)
- Apply micro-segmentation for high-value assets
Zero Trust architecture principles, detailed in Microsoft's Zero Trust Guidance, assume no implicit trust based on network location. Every access request undergoes verification regardless of origin, enforcing least-privilege principles throughout the network fabric. This approach particularly benefits organizations with remote workforces, cloud adoption, and third-party connections.
Operational Network Security and Management Practices
Strategic planning requires operational discipline to deliver sustained security outcomes. Daily network security and management activities encompass monitoring, configuration management, patch deployment, and incident response-each demanding clear ownership and documented procedures.
Continuous Monitoring and Threat Detection
Visibility into network traffic, device status, and user activity enables early threat detection. Security Information and Event Management (SIEM) platforms aggregate logs from firewalls, switches, routers, and endpoints, correlating events to surface suspicious patterns human analysts might miss.
Critical monitoring capabilities include:
- Real-time traffic analysis identifying command-and-control communications
- Behavioral analytics detecting deviations from normal patterns
- Automated alerting when policy violations occur
- Centralized logging supporting forensic investigation
- Performance metrics ensuring availability alongside security
Organizations considering managed security partnerships should clarify monitoring scope, alert prioritization, and response procedures. F&C's managed security services provide 24/7 response capabilities, though specific service levels vary based on engagement terms. Business leaders should establish clear expectations around notification timeframes, escalation paths, and remediation responsibilities.
Configuration Management and Hardening
Insecure configurations create easily exploited weaknesses. Network devices ship with default settings prioritizing ease of deployment over security, requiring deliberate hardening before production use.
The NIST SP 800-115 Technical Guide to Information Security Testing and Assessment provides methodology for validating configuration security through testing. Regular assessments verify hardening standards remain enforced as networks evolve.
| Device Type | Critical Hardening Steps | Common Vulnerabilities |
|---|---|---|
| Firewalls | Disable unused services, enforce strong authentication, restrict management access | Weak passwords, outdated firmware, overly permissive rules |
| Switches | Disable unused ports, implement port security, configure VLANs | Default passwords, unprotected management interfaces, VLAN hopping |
| Routers | Secure routing protocols, filter traffic, enable logging | Unencrypted management, missing access controls, inadequate monitoring |
| Wireless | Strong encryption (WPA3), network segmentation, client isolation | Weak passphrases, outdated encryption, rogue access points |
Automation tools using standards like YANG data modeling enable consistent, scalable configuration management across complex network environments. Intent-based networking translates business policies into device configurations, reducing manual errors while accelerating deployment.
Vulnerability Management and Testing
Proactive vulnerability identification prevents exploitation. Network security and management programs should incorporate regular vulnerability assessments, penetration testing, and remediation workflows addressing discovered weaknesses before attackers find them.
Vulnerability Assessment Programs
Automated scanning tools identify known vulnerabilities in network devices, services, and configurations. Regular scanning cadences-weekly or monthly depending on environment complexity-maintain current visibility as infrastructure changes and new vulnerabilities emerge.
Assessment scope should cover:
- External perimeter devices exposed to the internet
- Internal network infrastructure and services
- Wireless access points and controllers
- VPN gateways and remote access solutions
- Network management and monitoring systems
Vulnerability data requires prioritization considering exploitability, business impact, and compensating controls. Not every finding demands immediate patching; risk-based remediation allocates resources where they deliver maximum security improvement.
Penetration Testing for Network Security Validation
Penetration testing simulates attacker techniques against production networks, validating whether security controls withstand real-world attack scenarios. Unlike automated scanning, penetration tests employ manual techniques combining multiple vulnerabilities into exploit chains.
F&C's Managed VAPT and Forensics services tailor testing scope to business objectives, examining authorized systems through agreed methodologies that balance security validation against operational disruption. Organizations should define testing boundaries, acceptable techniques, and communication protocols before engagement begins.
Testing typically examines:
- External attack surface reachable from the internet
- Internal network security from compromised user perspective
- Wireless network security against common attacks
- Physical security protecting network infrastructure
- Social engineering targeting network access
Test findings inform remediation priorities and control improvements, creating measurable security maturation over successive testing cycles.
Cloud and Hybrid Network Security Considerations
Cloud adoption fundamentally changes network security and management. Traditional perimeter-focused controls prove insufficient when applications span on-premises data centers, public clouds, and SaaS platforms. Hybrid architectures require unified security policies enforced consistently across diverse environments.
Securing Cloud Network Infrastructure
Public cloud platforms provide native security capabilities-security groups, network ACLs, virtual firewalls-requiring proper configuration. The Cloud Security Alliance's Security Guidance v5 addresses infrastructure protection alongside identity, data, and application security specific to cloud deployment models.
Cloud network security priorities:
- Proper segmentation using virtual networks and subnets
- Strict security group rules limiting traffic to business needs
- Encrypted communications for data in transit
- Secure interconnections between cloud and on-premises networks
- Comprehensive logging for security monitoring and compliance
Shared responsibility models complicate accountability. Cloud providers secure underlying infrastructure; customers protect configurations, access controls, and workloads. Business decision-makers must clarify responsibility boundaries, ensuring no security gaps fall between provider and customer obligations.
Hybrid Network Architecture Security
Organizations rarely operate exclusively in cloud or on-premises environments. Hybrid architectures introduce complexity through multiple connection types, inconsistent control enforcement, and visibility challenges spanning environments.
Consistent policy enforcement across hybrid networks requires:
- Unified identity and access management spanning environments
- Centralized monitoring aggregating logs from all sources
- Standardized configuration baselines applied universally
- Network segmentation extending logically across physical boundaries
- Regular architecture reviews validating security as environments evolve
Compliance and Regulatory Considerations
Regulatory frameworks increasingly mandate specific network security and management controls. Organizations handling payment card data, healthcare information, or personal data face requirements around network segmentation, encryption, access logging, and vulnerability management.
Aligning Network Security with Compliance Requirements
PCI DSS, HIPAA, GDPR, and sector-specific regulations all include network security provisions. Compliance programs should map regulatory requirements to technical controls, documenting how network architecture and operational processes satisfy obligations.
Compliance and regulatory assessments help businesses understand applicable requirements and identify gaps requiring remediation. Structured approaches prevent compliance becoming reactive crisis management, instead integrating regulatory obligations into ongoing network security and management practices.
Common compliance-driven network controls include:
- Network segmentation isolating regulated data
- Multi-factor authentication for privileged network access
- Encryption protecting data in transit
- Comprehensive logging with defined retention periods
- Regular vulnerability scanning with documented remediation
- Penetration testing validating control effectiveness
Organizations pursuing ISO 27001 certification find network security controls integral to information security management systems. F&C's ISO 27001 implementation support helps businesses establish compliant network security processes within broader ISMS frameworks, preparing for independent assessment.
Technology Selection and Vendor Management
Network security and management technologies span firewalls, intrusion prevention systems, secure access solutions, monitoring platforms, and management tools. Selecting appropriate technologies requires understanding business requirements, risk priorities, and operational capabilities.
Evaluating Network Security Solutions
Technology evaluation should start with requirements rather than vendor capabilities. Define what problems need solving-unauthorized access, insufficient visibility, compliance gaps-then assess which solutions address those specific challenges within budget constraints.
| Evaluation Criterion | Questions to Ask | Impact on Decision |
|---|---|---|
| Capability Fit | Does this solve our priority security problems? | Eliminates mismatched solutions early |
| Scalability | Will this support growth over 3-5 years? | Prevents costly replacements |
| Integration | How does this work with existing systems? | Reduces complexity and costs |
| Manageability | Can our team operate this effectively? | Determines managed service needs |
| Total Cost | What are licensing, implementation, and operational costs? | Enables accurate budget planning |
Many organizations lack internal expertise to deploy and operate enterprise-grade network security technologies. Managed security providers bridge capability gaps, delivering expertise and 24/7 operations without building internal teams. Decision-makers should clarify what services include-monitoring, response, remediation, reporting-and what remains customer responsibility.
Licensing Models and Renewals
Network security products typically use subscription licensing covering software updates, threat intelligence feeds, and support. License renewals require advance planning to prevent capability lapses that create security gaps.
Licensing considerations include:
- Perpetual versus subscription models and total cost over time
- Feature tiers and which capabilities justify premium licensing
- Support levels and response timeframes for critical issues
- Renewal timing avoiding budget surprises
- Consolidation opportunities reducing vendor sprawl
Organizations should establish renewal calendars tracking license expiration dates, budget requirements, and decision milestones. F&C assists with Check Point licensing and renewals, though specific arrangements depend on whether licenses are purchased separately or included within managed service agreements. Business leaders should discuss requirements directly to understand available options.
Building Network Security Resilience
Network security and management extends beyond preventing initial compromise. Resilient networks assume breaches will occur, emphasizing rapid detection, effective containment, and swift recovery minimizing business impact.
Incident Response Preparedness
Documented incident response procedures accelerate effective action during network security events. Playbooks should define roles, communication channels, containment steps, and recovery procedures specific to network compromise scenarios.
Effective incident response includes:
- Initial triage determining scope and severity
- Containment isolating affected network segments
- Investigation identifying attack vectors and compromised systems
- Eradication removing attacker access and persistence mechanisms
- Recovery restoring normal operations with enhanced controls
- Lessons learned documenting improvements preventing recurrence
Organizations should conduct tabletop exercises testing incident response procedures against realistic scenarios. These exercises surface process gaps, clarify responsibilities, and build muscle memory before real incidents create pressure.
Business Continuity and Disaster Recovery
Network infrastructure failures-whether from attacks, hardware failures, or natural disasters-disrupt business operations. Continuity planning ensures critical business functions can continue despite network disruptions through redundancy, failover capabilities, and alternative access methods.
Recovery Time Objectives (RTO) and Recovery Point Objectives (RPO) quantify acceptable downtime and data loss, informing architecture decisions around redundancy, backup frequency, and failover automation. Business leaders should establish these targets based on operational requirements and financial impact of disruptions.
Effective network security and management protects business operations, customer trust, and regulatory compliance while enabling strategic initiatives requiring reliable, secure connectivity. Success demands clear risk understanding, appropriate control selection, operational discipline, and continuous adaptation as threats and business requirements evolve. F&C partners with organizations across Australia, New Zealand, the United States, and Dubai to build resilient network security programs tailored to business objectives, delivering managed security operations, vulnerability testing, and compliance expertise backed by professional certifications. Contact our team to discuss how we can support your network security and management requirements.