Protection Privacy: Essential Strategies for 2026
Protection privacy has evolved from a compliance checkbox into a strategic imperative for organizations operating across global markets. Business leaders in Australia, New Zealand, the United States, and Dubai face increasingly complex regulatory landscapes where personal information handling determines competitive advantage, customer trust, and regulatory standing. For decision-makers without dedicated internal security teams, understanding how to build effective protection privacy programs requires clarity on frameworks, technical controls, and sustainable governance approaches.
Understanding Protection Privacy in Modern Business Context
Protection privacy encompasses the policies, technologies, and processes that organizations deploy to safeguard personal information throughout its lifecycle. This discipline extends beyond simply preventing unauthorized access; it addresses how businesses collect, process, store, share, and ultimately dispose of data belonging to customers, employees, and partners.
The NIST Privacy Framework provides a structured approach that helps organizations manage privacy risk through five core functions: Identify, Govern, Control, Communicate, and Protect. These functions form the foundation for building programs that align business objectives with privacy obligations.
Regulatory Drivers Shaping Protection Privacy Requirements
Multiple regulatory regimes now influence how organizations must approach protection privacy. The General Data Protection Regulation establishes comprehensive requirements for businesses processing EU resident data, including lawful basis determination, data subject rights, and accountability obligations.
Australian organizations navigate the Privacy Act 1988 and its Australian Privacy Principles, which govern collection, use, disclosure, and security of personal information. United States businesses contend with sector-specific laws and state-level frameworks like the California Consumer Privacy Act. Dubai and broader UAE jurisdictions apply federal data protection law alongside emirate-specific requirements.
Key compliance considerations include:
- Lawful basis establishment for processing activities
- Data subject rights implementation (access, rectification, erasure)
- Cross-border transfer mechanisms and adequacy determinations
- Breach notification obligations and timeframes
- Records of processing activities maintenance
| Regulatory Framework | Primary Scope | Key Obligation | Penalty Structure |
|---|---|---|---|
| GDPR | EU resident data | Lawful basis, accountability | Up to 4% global revenue |
| Australian Privacy Act | Australian personal information | APPs compliance, notification | Up to AUD 50 million |
| CCPA/CPRA | California consumer data | Disclosure, deletion rights | Up to USD 7,500 per violation |
| UAE PDPL | UAE personal data | Consent, data security | Variable by emirate |
Building Technical Controls for Protection Privacy
Technical implementation transforms policy commitments into operational reality. Organizations require layered controls that address protection privacy across network infrastructure, applications, databases, and user endpoints.
Encryption serves as a fundamental control, rendering data unreadable without proper decryption keys. Organizations should implement encryption for data at rest (stored in databases, file systems, backups) and data in transit (moving across networks, transmitted to third parties). Modern encryption standards like AES-256 for symmetric encryption and RSA-2048 or higher for asymmetric encryption provide robust protection.
Access Control and Authentication Mechanisms
Protection privacy depends heavily on ensuring only authorized individuals access personal information. Role-based access control (RBAC) assigns permissions based on job functions rather than individual identities, simplifying administration while enforcing least-privilege principles.
Multi-factor authentication adds critical protection by requiring multiple verification methods before granting access. Combining something the user knows (password), something they have (mobile device, hardware token), and potentially something they are (biometric) significantly reduces unauthorized access risk.
The OWASP User Privacy Protection Cheat Sheet offers practical guidance for developers implementing privacy controls in applications, covering session management, data minimization, and secure communication channels.
Data masking and tokenization provide additional protection privacy mechanisms:
- Static masking permanently replaces sensitive data with fictitious but realistic values in non-production environments
- Dynamic masking shows different data views to users based on privileges without altering underlying stored data
- Tokenization replaces sensitive data with non-sensitive equivalents (tokens) that maintain relationships without exposing actual values
- Format-preserving encryption encrypts data while maintaining its original format for system compatibility
Privacy-Enhancing Technologies and Advanced Approaches
Privacy-enhancing technologies (PETs) enable organizations to extract value from data while minimizing privacy risks. ENISA's research on Privacy-Enhancing Technologies examines maturity frameworks and practical implementation guidance for these emerging capabilities.
Differential privacy adds statistical noise to datasets, ensuring individual records cannot be identified while maintaining overall data utility for analysis. Google Research demonstrates practical differential privacy deployments in machine learning models, showing how organizations can balance privacy protection with analytical insights.
Homomorphic encryption allows computations on encrypted data without decryption, enabling secure cloud processing and collaborative analytics. While computationally intensive, selective deployment for high-sensitivity scenarios provides strong protection privacy guarantees.
Implementing Privacy by Design Principles
Privacy by design embeds protection privacy into system architecture from inception rather than retrofitting controls after development. This proactive approach reduces compliance risk, development costs, and privacy debt accumulation.
Organizations implementing ISO 27701 Privacy Information Management Systems formalize privacy by design through structured controls aligned with ISO 27001 security foundations. This international standard provides requirements and guidance for establishing, implementing, maintaining, and continually improving privacy management systems.
Seven foundational privacy by design principles:
- Proactive rather than reactive; preventative rather than remedial
- Privacy as the default setting without user action required
- Privacy embedded into design specifications and architecture
- Full functionality through positive-sum rather than zero-sum approaches
- End-to-end security throughout the complete data lifecycle
- Visibility and transparency maintaining openness about practices
- Respect for user privacy through user-centric design
Governance Structures Supporting Protection Privacy
Effective protection privacy requires governance frameworks that define accountability, decision-making authority, and oversight mechanisms. Organizations should establish clear roles bridging business leadership, legal counsel, information technology, and operational functions.
A designated Data Protection Officer or Privacy Officer provides dedicated leadership, coordinating compliance activities, serving as regulatory contact point, and advising on privacy impact assessments. Even organizations not legally required to appoint a DPO benefit from centralized privacy accountability.
Privacy committees or steering groups bring together cross-functional stakeholders to review policies, assess risks, approve high-risk processing activities, and monitor program effectiveness. Regular meeting cadences ensure sustained attention rather than episodic focus triggered by incidents or audits.
Data Protection Impact Assessments
Data Protection Impact Assessments (DPIAs) systematically evaluate privacy risks before implementing new processing activities, systems, or technologies. The IAPP resources hub provides templates and practitioner guidance for conducting effective assessments.
DPIA workflow typically includes:
- Describing information flows and processing purposes
- Identifying necessity and proportionality considerations
- Assessing risks to individual rights and freedoms
- Determining mitigation measures and residual risk acceptance
- Documenting decisions and obtaining stakeholder approvals
- Reviewing periodically or when circumstances change
Organizations processing large volumes of sensitive personal data, conducting systematic monitoring, or deploying automated decision-making should prioritize DPIA implementation. These assessments demonstrate accountability while identifying protection privacy gaps before they manifest as compliance violations or reputational damage.
Third-Party Risk Management for Protection Privacy
Modern businesses rarely process data in isolation. Cloud service providers, payment processors, marketing platforms, and business process outsourcers create extended ecosystems requiring careful protection privacy oversight.
F&C helps organizations implement third-party supplier risk programs that evaluate vendor privacy capabilities before engagement and monitor ongoing compliance. This structured approach prevents supply chain weaknesses from undermining internal controls.
Vendor assessment questionnaires should address data handling practices, subprocessor arrangements, security certifications, breach notification procedures, and data subject rights fulfillment mechanisms. Contract provisions must clearly allocate responsibilities, establish audit rights, and define liability in case of privacy violations.
Due diligence depth should vary based on risk factors:
| Risk Factor | Low Risk | Medium Risk | High Risk |
|---|---|---|---|
| Data sensitivity | Non-personal metadata | Standard business contact information | Health records, financial data, biometrics |
| Processing volume | Minimal, occasional | Regular operational processing | Large-scale, continuous processing |
| Assessment frequency | Annual questionnaire | Semi-annual review plus attestation | Quarterly review plus onsite audit |
| Contract controls | Standard terms | Enhanced DPA with SCC | Comprehensive DPA plus insurance requirement |
Incident Response and Breach Management
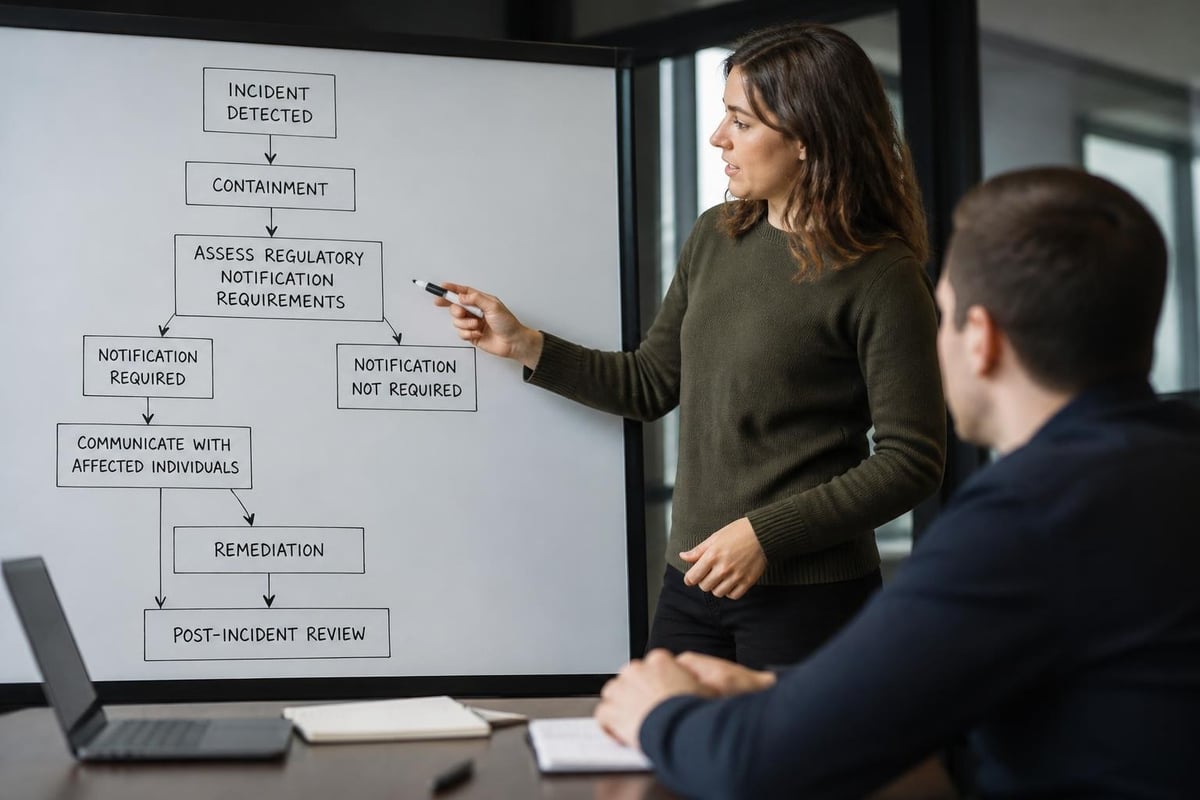
Despite preventive measures, organizations must prepare for privacy incidents through documented response plans, trained personnel, and tested procedures. NIST SP 800-61 Rev. 3 provides authoritative guidance for incident response with privacy considerations embedded throughout detection, analysis, containment, eradication, and recovery phases.
Protection privacy breach response differs from general security incidents through its focus on affected individuals, regulatory notification obligations, and reputational management. Organizations typically have limited timeframes to assess breach scope, notify regulators (often 72 hours under GDPR), and communicate with affected data subjects.
Establishing Response Procedures
Incident response plans should define trigger criteria for activation, assign specific roles (incident commander, communications lead, legal counsel, technical investigation), and provide decision trees for notification determinations.
Maintaining evidence throughout incident response supports regulatory inquiries, forensic analysis, and potential litigation. Chain of custody documentation, timestamped logs, and preservation of affected systems enable thorough investigation while demonstrating due diligence.
Post-incident activities strengthen protection privacy:
- Root cause analysis identifying control failures
- Remediation implementation addressing identified weaknesses
- Lessons learned documentation and team debrief
- Policy and procedure updates reflecting new understanding
- Training reinforcement for personnel on revised processes
Organizations should conduct tabletop exercises simulating breach scenarios to test response plans, identify gaps, and build muscle memory before facing actual incidents. These exercises reveal coordination challenges, communication bottlenecks, and decision-making uncertainties in low-stakes environments.
Measuring Protection Privacy Program Effectiveness
Business leaders require metrics demonstrating that protection privacy investments deliver expected outcomes. Measurement frameworks should combine leading indicators (predictive of future performance) with lagging indicators (recording past results).
Leading indicators include:
- Percentage of systems with completed DPIAs before deployment
- Staff completion rates for privacy awareness training
- Mean time to remediate identified privacy control gaps
- Third-party assessment completion rates within defined timeframes
Lagging indicators include:
- Number of privacy incidents and breaches over defined periods
- Data subject rights request fulfillment timeliness
- Regulatory examination findings and compliance violations
- Customer satisfaction scores regarding privacy practices
The Federal Trade Commission's Privacy and Data Security update provides regulatory perspective on enforcement trends and priorities, helping organizations understand where compliance focus should concentrate.
Continuous Improvement and Maturity Advancement
Protection privacy programs should evolve as business activities, technologies, and threat landscapes change. Organizations implementing governance frameworks and GRC strategy establish structured improvement cycles aligned with broader risk management objectives.
Maturity models help organizations assess current capabilities and chart progression paths. Early-stage programs typically focus on basic compliance and reactive incident response. Mature programs embed privacy into business strategy, leverage automation for monitoring and enforcement, and demonstrate measurable privacy outcomes influencing competitive positioning.
Regular internal audits examine control effectiveness, policy adherence, and procedure completeness. External assessments through independent auditors or certification bodies provide objective validation of program maturity. Organizations pursuing ISO 27701 implementation receive structured frameworks for continuous improvement aligned with international best practices.
Practical Implementation Considerations for Resource-Constrained Organizations
Decision-makers without dedicated security teams often question whether robust protection privacy remains achievable given resource limitations. Pragmatic approaches prioritize high-impact controls, leverage managed service partnerships, and phase implementation based on risk prioritization.
Starting points for protection privacy programs include:
- Inventorying personal data collected, processed, and stored across systems
- Documenting lawful bases and processing purposes for identified data
- Implementing basic access controls limiting data exposure
- Establishing data retention and deletion procedures
- Creating incident response contact lists and notification templates
Technology platforms increasingly embed privacy capabilities into core functionality, reducing custom development requirements. Cloud providers offer encryption, access logging, and automated retention management. Email and productivity suites include data loss prevention and rights management features.
Managed service providers like F&C extend internal capabilities through specialized expertise, continuous monitoring, and shared responsibility models. Organizations gain access to certified professionals, established methodologies, and proven control frameworks without building internal departments.
Partnership models should clearly define responsibility boundaries, establish communication protocols, and create accountability mechanisms through service level agreements. Regular reviews ensure managed services evolve alongside changing business requirements and emerging threats.
Training and Awareness Building Protection Privacy Culture
Technology and process controls ultimately depend on personnel understanding privacy obligations and making sound decisions when handling personal information. Organizations should implement layered training addressing different audiences with role-specific content.
General awareness training introduces all personnel to basic protection privacy concepts, organizational policies, incident reporting procedures, and individual responsibilities. Annual refresher training reinforces concepts while addressing emerging topics like artificial intelligence implications or new regulatory requirements.
Specialized training for developers, system administrators, and data analysts covers technical implementation of privacy controls, secure coding practices, and privacy by design principles. Role-based scenarios help technical personnel recognize privacy implications in daily activities.
Leadership training equips managers and executives to make informed decisions balancing business objectives with privacy requirements, understand regulatory obligations affecting strategic initiatives, and model privacy-conscious behavior throughout organizations.
Organizations pursuing security awareness training programs should integrate privacy modules alongside general cybersecurity content, recognizing overlapping control objectives and shared cultural foundations.
Measuring Training Effectiveness
Training investments should demonstrate measurable impact beyond completion certificates. Organizations can track privacy incident rates attributable to human error, phishing simulation click rates for privacy-themed attacks, and correct response rates in scenario-based assessments.
Periodic knowledge checks embedded within workflows reinforce learning while providing performance data. For example, systems might present brief privacy questions when users access sensitive data, collect personal information through forms, or configure new applications.
Positive reinforcement programs recognize individuals and teams demonstrating strong protection privacy practices, share success stories of prevented incidents, and celebrate compliance milestones. Building privacy champions within business units extends formal training through peer influence and informal mentoring.
Protection privacy programs succeed when organizations move beyond compliance minimums toward strategic integration of privacy into business operations. Decision-makers benefit from structured frameworks, proven technologies, and clear governance while maintaining flexibility to address unique business contexts and risk profiles. F&C brings comprehensive cybersecurity and compliance expertise to organizations building protection privacy capabilities, offering managed services, specialized assessments, and long-term partnerships that extend internal resources with certified professionals and proven methodologies. Contact F&C to discuss how managed privacy and security services can help your organization build resilient protection privacy programs aligned with business objectives.