Risk Management and Cybersecurity: A Complete Guide
Risk management and cybersecurity are no longer separate disciplines. In 2026, businesses face an evolving threat landscape where a single vulnerability can cascade into operational disruption, regulatory penalties, and reputational damage. Organizations without dedicated security teams must understand how to identify risks, prioritize controls, and build resilience without overwhelming their resources. This guide explains the principles, frameworks, and practical steps that connect risk management to effective cybersecurity protection.
Understanding the Connection Between Risk and Security
Risk management provides the structured approach that makes cybersecurity decisions measurable and defensible. Rather than reacting to every alert or deploying tools without strategy, risk management asks which assets matter most, where vulnerabilities exist, and what controls deliver the greatest reduction in exposure.
Cybersecurity becomes the implementation layer. It translates risk priorities into technical and procedural safeguards. Firewalls, access controls, encryption, and incident response plans all serve a single purpose: reducing the likelihood or impact of identified risks.
The NIST Cybersecurity Framework 2.0 formalizes this connection. Its six core functions-Govern, Identify, Protect, Detect, Respond, and Recover-map directly to the risk management cycle. Governance establishes accountability and risk appetite. Identification catalogs assets and threats. Protection, detection, and response implement controls. Recovery measures resilience.
Why Businesses Without Security Teams Need This Approach
Decision-makers in growing organizations often inherit cybersecurity responsibilities without specialized training. Risk management offers a language and structure that bridges technical complexity and business priorities.
Key benefits include:
- Resource allocation: Focus spending on controls that address your highest-value assets and most probable threats
- Regulatory alignment: Demonstrate due diligence to auditors, clients, and regulators through documented risk treatment
- Scalability: Build a program that grows with your business rather than requiring constant overhaul
Without this connection, security becomes a collection of tools that may not address your actual exposure. Risk management and cybersecurity must work together to create a coherent defense.
Identifying and Assessing Cybersecurity Risks
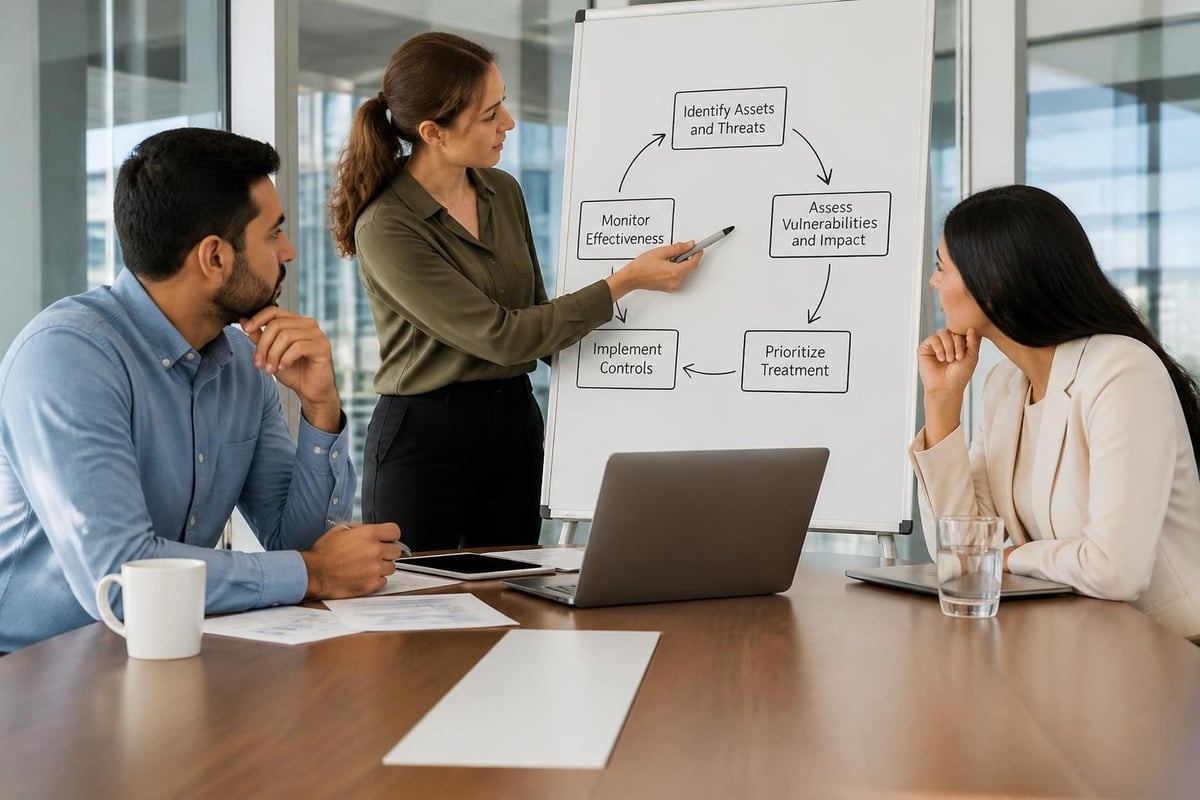
Risk identification begins with asset inventory. What information, systems, and processes are essential to your operations? Which ones, if compromised, would halt revenue, breach contracts, or expose sensitive data?
Building an Asset Register
An asset register documents each system, data set, and business process within scope. For each asset, record its owner, location, dependencies, and classification. Classification typically uses tiers such as public, internal, confidential, and restricted.
This register becomes the foundation for every subsequent risk decision. You cannot protect what you have not identified.
| Asset Type | Examples | Common Vulnerabilities |
|---|---|---|
| Data | Customer records, financial data, intellectual property | Insufficient encryption, weak access controls, unpatched databases |
| Systems | Email servers, cloud platforms, payment gateways | Misconfigurations, outdated software, inadequate logging |
| Processes | Invoice approval, client onboarding, incident response | Manual errors, lack of segregation, missing documentation |
Cataloging Threats and Vulnerabilities
Threats are external or internal actors and events that could exploit a weakness. The ENISA Threat Landscape 2025 provides current analysis of ransomware, supply chain attacks, phishing, and denial-of-service trends. Understanding which threats target your sector helps prioritize controls.
Vulnerabilities are the specific weaknesses that threats exploit. These include unpatched software, misconfigured cloud storage, weak passwords, and untrained staff. Vulnerability assessment and penetration testing examine these weaknesses systematically. Managed VAPT and Forensics services tailor testing to your business objectives, assets, and realistic attack scenarios, helping you understand exposure before adversaries exploit it.
Evaluating Likelihood and Impact
Once threats and vulnerabilities are cataloged, assess each risk using likelihood and impact. Likelihood considers factors such as threat actor motivation, your external exposure, and existing control effectiveness. Impact measures the financial, operational, legal, and reputational consequences of successful exploitation.
A simple 3x3 or 5x5 matrix plots each risk. High-likelihood, high-impact risks demand immediate treatment. Low-likelihood, low-impact risks may be accepted. This prioritization ensures limited resources address your most significant exposures first.
Implementing Risk Treatment and Security Controls
Risk treatment selects the appropriate response for each identified risk. The four standard options are avoidance, mitigation, transfer, and acceptance.
Avoidance eliminates the risk by discontinuing the activity. If a legacy system cannot be secured and is not essential, decommissioning it removes the exposure entirely.
Mitigation reduces likelihood or impact through controls. Most cybersecurity efforts fall into this category. Examples include deploying firewalls, enforcing multi-factor authentication, encrypting data at rest and in transit, and training staff to recognize phishing.
Transfer shifts financial consequences to another party, typically through cyber insurance or contractual indemnification. Transfer does not eliminate the risk, but it can reduce financial impact.
Acceptance acknowledges risks that cost more to mitigate than their expected loss. Document these decisions and review them periodically as your risk profile evolves.
Prioritizing Controls with Established Frameworks
Frameworks provide tested blueprints for control selection. The CIS Controls v8.1 organizes safeguards into Implementation Groups based on organizational size and resources. Small businesses with limited IT staff begin with foundational controls such as asset inventory, access management, and data protection before progressing to advanced measures.
MITRE ATT&CK maps adversary tactics and techniques to specific defenses. By understanding how attackers move through your environment-from initial access to lateral movement to data exfiltration-you can prioritize detection and response controls that disrupt their progress.
ISO/IEC 27001 takes a different approach. It establishes an Information Security Management System (ISMS) that embeds risk management into governance, policy, and continuous improvement. Organizations pursuing certification or client assurance often adopt this standard. F&C supports ISO 27001:2022 ISMS Implementation aligned with your risk profile and prepares you for independent assessment.
Integrating Governance and Accountability
Risk management and cybersecurity require clear ownership. Assign a senior executive accountability for information security, even if day-to-day tasks are outsourced. Define roles for risk assessment, control implementation, incident response, and audit coordination.
Document policies, standards, and procedures that translate risk decisions into repeatable actions. Governance frameworks and GRC strategy services help establish these structures in a way that scales with your business and meets regulatory expectations.
Monitoring, Measuring, and Adapting Risk Posture
Risk management is continuous. Threat actors evolve. Your business introduces new technologies. Regulations change. Static risk assessments become outdated within months.
Establishing Metrics and Indicators
Metrics quantify control effectiveness and residual risk. Common examples include:
- Vulnerability remediation time: Average days between discovery and patch deployment
- Phishing test failure rate: Percentage of staff who click simulated phishing links
- Mean time to detect (MTTD): Average duration between intrusion and identification
- Mean time to respond (MTTR): Average duration between detection and containment
Track these metrics over time. Trends reveal whether your risk posture improves or deteriorates. Share summarized results with leadership to support investment decisions and accountability.
Continuous Threat Exposure Management
Threat exposure evolves as your attack surface changes. New cloud services, remote access points, third-party integrations, and application deployments introduce vulnerabilities. Continuous Threat Exposure Management identifies, prioritizes, and tracks these exposures in real time, ensuring controls adapt as your environment changes.
Regular vulnerability scanning, penetration testing, and security audits validate that implemented controls function as intended. Control effectiveness assessment services test whether safeguards meet design expectations and reduce risk to acceptable levels.
Incident Response and Lessons Learned
Even well-managed risks occasionally materialize. Incident response planning defines roles, communication protocols, containment procedures, and recovery steps before an event occurs.
After any incident-successful attack, near-miss, or drill-conduct a lessons-learned review. Identify root causes, control failures, and process gaps. Update risk registers, treatment plans, and controls accordingly. This feedback loop transforms incidents into risk management improvements.
Addressing Third-Party and Supply Chain Risks
Your organization's security depends on vendors, cloud providers, and business partners. Third-party risks are among the most challenging to manage because you control neither their environments nor their practices.
Vendor Risk Assessment and Contractual Controls
Before engaging a vendor, assess their security posture. Request evidence of certifications (ISO 27001, SOC 2), policies, incident history, and data handling practices. Evaluate whether their controls align with the sensitivity of data they will access or process.
Contracts should define security obligations, breach notification timelines, audit rights, and liability. Third-party and supplier risk services help structure these assessments and ensure vendors meet your risk appetite.
Monitoring Vendor Performance
Due diligence does not end at contract signature. Monitor vendor security through periodic reviews, audits, and control testing. If a vendor suffers a breach or regulatory action, reassess their risk and consider mitigation or exit strategies.
Supply chain attacks exploit trusted relationships. Adversaries compromise a vendor to gain access to multiple downstream organizations. Understanding these dependencies and implementing controls such as network segmentation, least-privilege access, and behavioral monitoring reduces your exposure.
Regulatory Compliance and Risk Management Integration
Compliance frameworks mandate specific controls, but they also reflect collective risk management wisdom. Regulations such as GDPR, HIPAA, PCI DSS, and Australia's Privacy Act impose obligations that align closely with sound risk practices.
Mapping Regulations to Risk Controls
Rather than treating compliance as a separate checklist, integrate regulatory requirements into your risk register. For example, GDPR's data protection principles map to risks around unauthorized access, data loss, and breach notification. Controls that mitigate these risks simultaneously support compliance.
Compliance and regulatory assessments evaluate your alignment with applicable frameworks and identify gaps. Remediation becomes a risk treatment exercise, prioritized by both regulatory penalty and operational impact.
Evidence, Audit Readiness, and Documentation
Regulators and auditors demand evidence that controls exist and function effectively. Maintain logs, policies, test results, training records, and incident reports as proof of due diligence.
Evidence and audit readiness services organize this documentation in a way that accelerates audits, certifications, and client assurance reviews. Structured evidence collection also supports internal decision-making by revealing trends and control gaps.
Practical Steps to Start Your Risk Management Program
Building a risk management and cybersecurity program from scratch can feel overwhelming. These steps provide a pragmatic starting point for organizations without dedicated security teams.
1. Define your scope and objectives. What assets, systems, and processes will your program cover? What outcomes do you need-regulatory compliance, client assurance, operational resilience?
2. Inventory your assets. Document systems, data, and critical processes. Classify them by sensitivity and business impact.
3. Conduct an initial risk assessment. Identify threats and vulnerabilities relevant to your industry and asset inventory. Evaluate likelihood and impact using a simple matrix.
4. Prioritize and treat risks. Select treatment options for high-priority risks. Implement controls using established frameworks such as CIS or ISO 27001.
5. Document policies and assign ownership. Create policies that define acceptable use, access management, incident response, and vendor oversight. Assign accountability to specific roles.
6. Monitor and improve. Establish metrics, schedule periodic reviews, and update your risk register as your business and threat landscape evolve.
F&C's governance, risk, and compliance services support each of these steps with expertise tailored to your business context, helping you build a program that scales with your growth.
Frequently Asked Questions
How often should we reassess cybersecurity risks?
At minimum, conduct a comprehensive risk assessment annually. Review high-priority risks quarterly or whenever significant changes occur-new systems, mergers, major incidents, or regulatory updates. Continuous vulnerability scanning and threat monitoring provide ongoing risk visibility between formal assessments.
What is the difference between inherent and residual risk?
Inherent risk is the exposure before any controls are applied. Residual risk is what remains after controls are implemented. Risk treatment aims to reduce residual risk to an acceptable level, defined by your organization's risk appetite.
Can small businesses manage cybersecurity risk without a dedicated team?
Yes. Many small and mid-sized organizations lack in-house security staff but successfully manage risk by partnering with managed service providers, adopting frameworks tailored to their size, and prioritizing controls that address their highest exposures. Outsourcing specialized functions such as vulnerability testing, monitoring, and compliance allows you to access expertise without building an internal team.
How does risk management support cyber insurance applications?
Insurers evaluate your security posture before issuing policies. Documented risk assessments, control implementation, and incident response plans demonstrate due diligence and can improve coverage terms or reduce premiums. Conversely, poor risk management may result in exclusions or higher costs.
What role does employee training play in risk management?
Human error contributes to many cybersecurity incidents. Security awareness training reduces the likelihood of phishing, social engineering, and policy violations. Training is a cost-effective control that addresses multiple risk scenarios simultaneously.
Effective risk management and cybersecurity require a structured approach that identifies threats, prioritizes controls, and adapts to change. Businesses without dedicated security teams can build resilient programs by leveraging established frameworks, outsourcing specialized functions, and embedding risk decisions into governance. F&C helps organizations across Australia, New Zealand, the US, and Dubai understand their risks, implement practical controls, and build long-term security partnerships. Contact F&C to discuss how our managed cybersecurity and compliance services can support your risk management objectives.