Cyber Compliance: Essential Guide for Business Leaders
Organizations face mounting pressure to demonstrate effective cybersecurity practices while meeting an expanding set of regulatory obligations. Cyber compliance represents the intersection of security controls, risk management, and regulatory requirements that businesses must navigate to protect sensitive data, maintain customer trust, and avoid significant penalties. For decision-makers without dedicated security teams, understanding how to approach cyber compliance systematically can determine whether your organization thrives or struggles under regulatory scrutiny.
Understanding Cyber Compliance in the Modern Business Environment
Cyber compliance encompasses the policies, procedures, and technical controls organizations implement to meet specific regulatory, contractual, or industry standards for information security. Unlike general security practices, cyber compliance establishes measurable criteria against which auditors and regulators assess your organization's security posture.
The landscape has expanded significantly beyond traditional frameworks. Organizations now contend with privacy regulations like GDPR, sector-specific requirements such as PCI DSS for payment processors, and emerging mandates addressing ransomware response and supply chain security. Each framework brings distinct obligations, reporting timelines, and potential consequences for non-compliance.
Why Business Leaders Should Prioritize Cyber Compliance
Financial protection stands as the most immediate benefit. Regulatory fines for data breaches can reach millions of dollars, while contractual penalties from clients often compound these costs. Cyber compliance programs reduce exposure by implementing preventive controls and demonstrating due diligence.
Operational resilience improves when compliance frameworks drive structured risk management. The NIST Cybersecurity Framework provides a risk-based approach that helps organizations identify critical assets, protect essential functions, detect incidents promptly, respond effectively, and recover operations efficiently.
Market differentiation emerges as clients increasingly require proof of security maturity. Certifications and attestations demonstrate commitment to protecting customer data and maintaining service availability, often becoming prerequisites for enterprise contracts.
Key Regulatory Frameworks Shaping Cyber Compliance Requirements
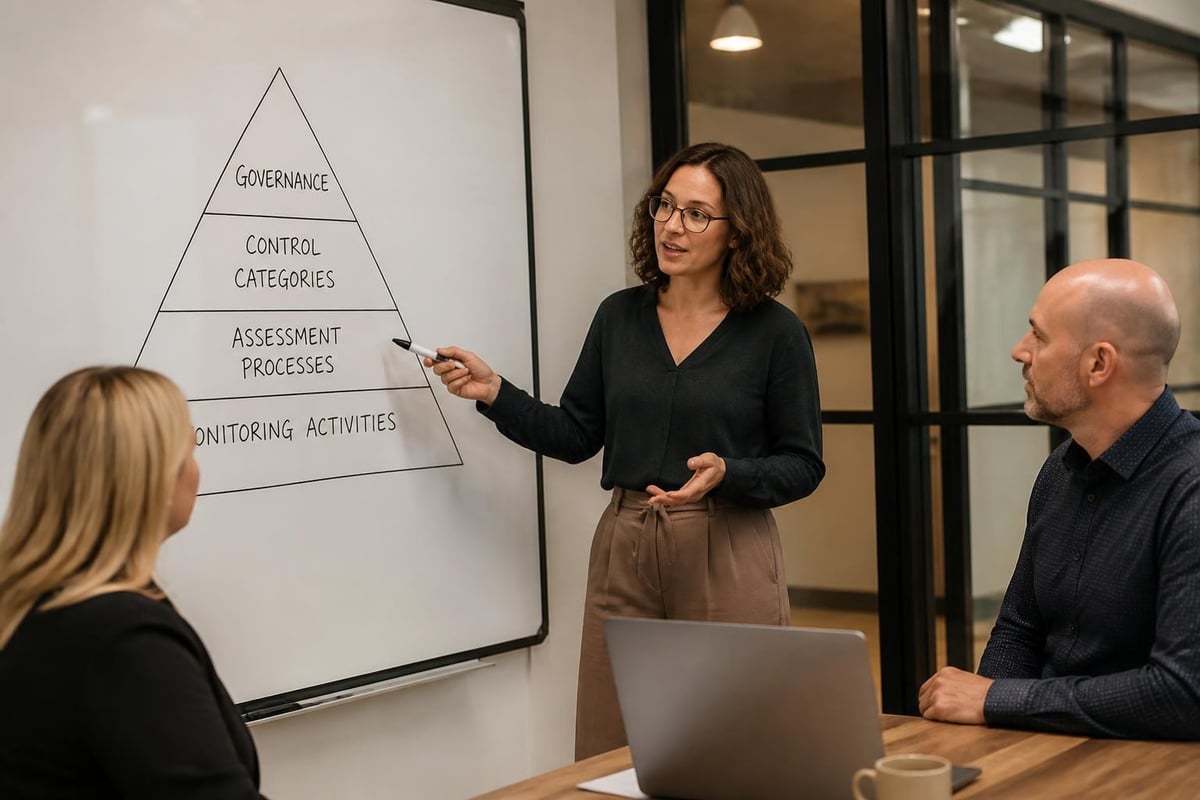
Different industries and regions mandate specific compliance obligations. Understanding which frameworks apply to your business determines your baseline security requirements and audit preparation needs.
| Framework | Primary Scope | Key Requirements | Geographic Reach |
|---|---|---|---|
| GDPR | Personal data processing | Consent, data rights, breach notification | EU and processors worldwide |
| PCI DSS v4.0 | Payment card data | Network segmentation, encryption, access controls | Global payment processors |
| ISO 27001 | Information security management | Risk assessment, control implementation, audit | International standard |
| SOC 2 | Service provider controls | Trust Services Criteria across security domains | Primarily North America |
| NIS2 Directive | Critical infrastructure | Incident response, supply chain security | European Union operators |
The PCI DSS v4.0 requirements introduced significant changes in 2026, particularly around customized implementation approaches and continuous validation. Organizations must now demonstrate ongoing compliance rather than point-in-time assessments, fundamentally changing how cyber compliance programs operate.
Compliance Obligations for Small and Medium Businesses
Many decision-makers assume regulatory frameworks apply only to large enterprises. This misconception creates significant risk. Most privacy regulations and contractual security requirements apply regardless of organization size, based instead on data types processed and services provided.
Payment processors, healthcare providers, and financial services firms face mandatory compliance regardless of employee count. Even organizations outside regulated sectors encounter compliance requirements through client contracts, particularly when serving enterprise customers or government agencies.
The compliance regulatory assessments process helps organizations identify applicable requirements and prioritize implementation based on actual risk and business impact rather than attempting to address every possible framework simultaneously.
Building an Effective Cyber Compliance Program
Successful cyber compliance programs balance regulatory requirements with operational realities. Organizations without internal security teams benefit from structured approaches that leverage external expertise while maintaining ownership of strategic decisions.
Essential Program Components
- Scope definition establishes boundaries for compliance efforts, identifying systems, data types, and processes subject to each regulatory framework
- Gap assessment compares current security posture against required controls, quantifying remediation efforts and timeline requirements
- Control implementation addresses identified gaps through technical solutions, policy updates, and process improvements
- Evidence collection documents controls and their operation, creating the foundation for audit readiness
- Continuous monitoring tracks control effectiveness and identifies drift from compliant configurations
Organizations frequently underestimate evidence collection requirements. Auditors require documented proof that controls operate as designed, including configuration records, access logs, training completion records, and incident response activities.
Selecting Controls That Address Multiple Frameworks
Smart organizations implement controls that satisfy requirements across multiple frameworks simultaneously. Encryption, access management, and monitoring capabilities typically address obligations in GDPR, PCI DSS, ISO 27001, and SOC 2, maximizing efficiency.
The governance frameworks approach maps individual controls to specific regulatory requirements, helping decision-makers understand which investments deliver the broadest compliance coverage. This strategic view prevents duplicative efforts and reduces total cost of ownership for cyber compliance programs.
- Multi-factor authentication satisfies access control requirements in virtually every framework
- Encryption at rest and in transit addresses data protection mandates across privacy and security standards
- Centralized logging supports incident detection, forensic analysis, and compliance reporting obligations
- Regular vulnerability scanning meets assessment requirements while improving overall security posture
- Documented policies establish governance expectations required by auditors and regulators
Common Cyber Compliance Challenges and Practical Solutions
Organizations encounter predictable obstacles when building cyber compliance capabilities. Recognizing these challenges early enables proactive planning and resource allocation.
Resource Constraints and Expertise Gaps
Most businesses lack sufficient internal expertise to interpret regulatory requirements, select appropriate controls, and prepare for audits. The technical depth required for frameworks like ISO 27001 ISMS implementation often exceeds what generalist IT teams can deliver alongside operational responsibilities.
Managed cybersecurity services address this gap by providing access to certified professionals who understand regulatory nuances, control selection, and auditor expectations. Organizations maintain strategic control while leveraging specialized expertise for implementation and ongoing compliance management.
Keeping Pace with Regulatory Changes
Cyber compliance requirements evolve continuously as threats emerge and regulators refine expectations. The NIS2 Directive expanded scope and obligations significantly in 2023, requiring organizations operating in or with the EU to reassess their compliance posture.
Structured monitoring processes track regulatory updates, assess impact on existing controls, and prioritize necessary adjustments. This proactive approach prevents surprise compliance gaps discovered during audits.
Demonstrating Control Effectiveness
Implementing controls proves easier than demonstrating their effectiveness over time. Auditors require evidence showing controls operate consistently, detect relevant threats, and prompt appropriate responses when triggered.
| Control Type | Implementation Evidence | Effectiveness Evidence |
|---|---|---|
| Access Management | Configuration screenshots, policy documents | Access logs, privilege reviews, termination records |
| Encryption | Certificate inventories, system configurations | Key rotation logs, failed connection attempts |
| Vulnerability Management | Scanning schedules, tool configurations | Scan results, remediation tracking, exception approvals |
| Incident Response | Documented procedures, team assignments | Response logs, communication records, lessons learned |
Organizations pursuing formal certifications require particularly robust evidence collection. The certification surveillance readiness process ensures documentation meets auditor expectations while remaining manageable for ongoing operations.
Cyber Compliance and Incident Response Integration
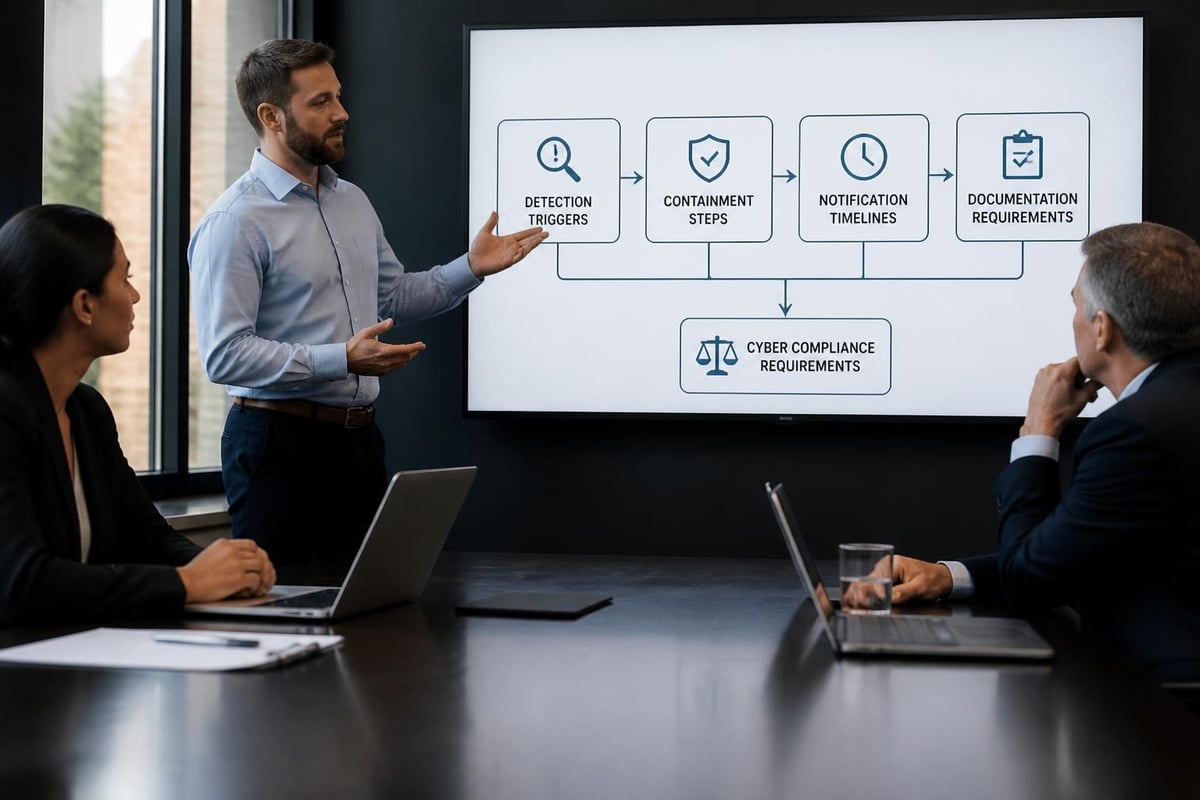
Regulatory frameworks increasingly emphasize incident response capabilities as a core compliance requirement. Organizations must detect security events, contain threats, notify affected parties, and document response activities within specified timeframes.
The CISA ransomware guidance outlines practical steps for preventing, responding to, and reporting ransomware incidents that often trigger regulatory notification obligations. Cyber compliance programs should incorporate these operational capabilities rather than treating incident response as a separate concern.
Notification Timelines and Reporting Obligations
Different frameworks impose varying notification requirements that organizations must track and meet simultaneously when multiple regulations apply:
- GDPR requires notification to supervisory authorities within 72 hours of becoming aware of a personal data breach
- PCI DSS mandates immediate notification to payment brands and acquirers for suspected card data compromise
- SOC 2 expectations include timely communication to affected clients when security incidents impact service delivery
- Sector-specific regulations often impose additional reporting obligations to industry regulators
Organizations need documented processes identifying who makes notification decisions, which stakeholders receive incident updates, and how evidence gets preserved for regulatory review. These capabilities directly support cyber compliance objectives while strengthening overall security posture.
The Role of Third-Party Risk in Cyber Compliance
Regulators increasingly hold organizations accountable for security practices of vendors, suppliers, and service providers who access sensitive data or deliver critical functions. Cyber compliance programs must extend beyond organizational boundaries to assess and manage third-party risk.
Vendor Security Assessment Requirements
Most compliance frameworks require documented third-party risk management processes. Organizations must evaluate vendor security controls before engagement, monitor ongoing compliance, and maintain evidence of vendor assessments.
The third-party supplier risk management process typically includes:
- Security questionnaire distribution to potential vendors
- Evidence review of certifications and attestations (SOC 2, ISO 27001)
- Contractual security requirements and audit rights
- Periodic reassessment based on criticality and risk
- Incident response coordination procedures
Organizations should prioritize vendor assessments based on data sensitivity and operational criticality rather than attempting comprehensive reviews of every supplier simultaneously.
Measuring Cyber Compliance Program Maturity
Effective cyber compliance programs evolve from reactive audit preparation to proactive risk management integrated with business operations. Understanding maturity levels helps organizations set realistic improvement goals and demonstrate progress to stakeholders.
Maturity Progression Stages
Initial stage organizations respond to specific compliance requirements reactively, often preparing for audits without sustained control operation between assessments. Documentation exists primarily for auditor review rather than operational use.
Developing stage businesses implement documented processes covering key regulatory requirements. Controls operate consistently, though evidence collection remains manual and time-consuming.
Defined stage organizations maintain comprehensive cyber compliance programs with integrated monitoring, automated evidence collection, and regular management reviews. Compliance becomes embedded in operational workflows rather than separate activities.
Optimized stage businesses demonstrate continuous improvement through metrics, trend analysis, and proactive control enhancement. Cyber compliance supports strategic objectives including market expansion, product development, and risk reduction.
The continual improvement programs approach helps organizations progress through maturity stages systematically, addressing capability gaps that limit compliance effectiveness.
Practical Steps for Starting Your Cyber Compliance Journey
Business leaders often delay cyber compliance initiatives due to perceived complexity and resource requirements. Breaking the process into manageable phases reduces overwhelm while building momentum toward full compliance.
Immediate Actions for Decision-Makers
Identify applicable requirements by reviewing contractual obligations, industry regulations, and geographic mandates based on your business operations and customer base. Many organizations discover compliance requirements through client security questionnaires or contract redlines that highlight gaps in current practices.
Document existing controls before assuming comprehensive implementation is necessary. Organizations often maintain stronger security practices than they realize, lacking only documentation and evidence collection to demonstrate compliance. This inventory prevents duplicative investments and identifies true gaps requiring attention.
Prioritize based on risk and business impact rather than attempting simultaneous compliance with every applicable framework. Payment processing businesses should address PCI DSS first, while service providers pursuing enterprise contracts benefit most from SOC 2 readiness.
The governance frameworks and GRC strategy service helps organizations establish priorities aligned with business objectives while meeting regulatory obligations efficiently.
Building Sustainable Compliance Capabilities
Long-term success requires embedding cyber compliance into business operations rather than treating it as a periodic audit exercise. Organizations should establish:
- Clear ownership for compliance domains, assigning specific individuals responsibility for control operation and evidence collection
- Integration points connecting compliance activities with existing workflows, such as incorporating security reviews into procurement processes
- Monitoring dashboards tracking control effectiveness metrics that inform management decisions
- Regular reviews examining compliance posture against evolving requirements and emerging risks
Organizations frequently discover that external support accelerates initial implementation while internal teams develop capability over time. This hybrid approach balances expertise requirements with long-term sustainability and cost management.
Technology Solutions Supporting Cyber Compliance Objectives
While cyber compliance fundamentally addresses governance and risk management, technology platforms significantly improve efficiency, consistency, and evidence quality. Decision-makers should understand which capabilities deliver the greatest compliance value.
Essential Platform Capabilities
| Capability | Compliance Benefit | Implementation Priority |
|---|---|---|
| SIEM/Log Management | Centralized evidence, incident detection, audit trails | High for most frameworks |
| Vulnerability Scanning | Systematic assessment, remediation tracking, audit proof | High for technical environments |
| GRC Platforms | Control mapping, evidence collection, workflow automation | Medium, scales with complexity |
| Identity Management | Access controls, privilege governance, termination workflows | High for data protection |
| Configuration Management | Baseline enforcement, drift detection, change tracking | Medium, critical for infrastructure |
Organizations should select technology investments based on specific compliance requirements rather than comprehensive platforms that exceed actual needs. A payment processor requires different capabilities than a software development firm, even when both pursue ISO 27001 certification.
The managed security operations approach provides access to enterprise-grade platforms and expert operation without capital investment in tools that require specialized expertise to operate effectively.
Cyber Compliance as Business Enabler Rather Than Cost Center
Forward-thinking organizations recognize cyber compliance programs as strategic assets that enable business growth, reduce operational risk, and differentiate market positioning. This perspective shift transforms how decision-makers approach compliance investments and measure program success.
Quantifiable Business Benefits
Contract expansion becomes possible when certifications and attestations satisfy customer security requirements. Enterprise buyers increasingly require SOC 2 reports or ISO 27001 certificates before engaging new service providers, particularly for cloud-based solutions or data processing services.
Insurance premiums decrease when organizations demonstrate mature cyber compliance programs. Insurers recognize that documented controls, regular testing, and incident response capabilities reduce claim likelihood and severity, translating these risk reductions into premium discounts.
Operational efficiency improves as compliance-driven processes eliminate security gaps that previously caused production incidents, data losses, or customer service disruptions. The discipline required for cyber compliance often reveals process weaknesses that impact business operations beyond regulatory concerns.
F&C helps organizations implement information security management systems that satisfy compliance requirements while strengthening overall security posture. The ISO 27001:2022 ISMS Implementation service delivers a structured approach to building governance frameworks, implementing controls, and preparing for independent assessment.
Addressing Common Misconceptions About Cyber Compliance
Decision-makers often hold inaccurate beliefs about cyber compliance that delay necessary investments or result in ineffective programs. Correcting these misconceptions enables better strategic planning and resource allocation.
Compliance Does Not Equal Security
Organizations sometimes assume achieving compliance automatically delivers comprehensive security. While compliance frameworks establish baseline security requirements, they represent minimum obligations rather than complete protection against all threats.
Cyber compliance programs should form the foundation for broader security initiatives that address organization-specific risks, emerging threats, and industry best practices beyond regulatory minimums. The information security risk management process identifies gaps between compliance requirements and actual security needs.
One-Time Implementation Is Insufficient
Cyber compliance requires ongoing operation, monitoring, and improvement rather than point-in-time achievement. Controls drift from compliant configurations, personnel changes affect process execution, and regulatory updates introduce new requirements that demand program adjustments.
Organizations need sustained capability to maintain compliance between audits, respond to regulatory changes, and demonstrate continuous control effectiveness. This operational reality often surprises businesses accustomed to project-based IT initiatives with defined endpoints.
External Support Does Not Mean Loss of Control
Some decision-makers resist managed cybersecurity services due to concerns about surrendering control over critical security functions. Professional service delivery actually provides greater transparency and control through defined processes, regular reporting, and clear accountability structures.
The managed VAPT and forensics service demonstrates this principle by delivering specialized testing capabilities while maintaining client control over scope, timing, and remediation priorities. Organizations gain expert execution without sacrificing strategic decision authority.
Future Trends Shaping Cyber Compliance Requirements
Regulatory environments continue evolving in response to emerging technologies, sophisticated threats, and high-profile security incidents. Business leaders should anticipate several trends that will influence cyber compliance programs through 2026 and beyond.
Artificial Intelligence Governance
Regulators worldwide are developing frameworks addressing AI system security, bias, transparency, and data protection. Organizations deploying AI capabilities will face new compliance obligations covering model training data, algorithmic decision-making, and automated processing of personal information.
The AI governance and risk management approach helps organizations establish governance frameworks before mandatory requirements emerge, positioning businesses to demonstrate responsible AI practices proactively.
Supply Chain Security Mandates
Recent incidents highlighting supply chain vulnerabilities have prompted regulatory focus on third-party risk management, software bill of materials requirements, and vendor security attestations. Organizations should expect expanding obligations around supplier assessments and contractual security controls.
Continuous Compliance Validation
The shift from periodic audits to continuous monitoring continues across frameworks. Organizations must implement capabilities that provide real-time visibility into control effectiveness rather than demonstrating compliance only during scheduled assessments.
Cyber compliance represents both regulatory obligation and strategic opportunity for organizations seeking to protect sensitive data, maintain customer trust, and compete effectively in security-conscious markets. By approaching compliance systematically through risk assessment, control implementation, and continuous monitoring, businesses build resilience against evolving threats while meeting regulatory expectations. F&C delivers comprehensive cybersecurity and compliance services that help organizations understand requirements, implement effective controls, and maintain compliance through ongoing support and expert guidance. Contact us to discuss how we can support your compliance objectives.