Cybersecurity Management: A Complete Guide for 2026
Cybersecurity management represents the structured approach organizations take to identify, assess, control, and monitor information security risks across their operations. As digital transformation accelerates in 2026, businesses face increasingly sophisticated threats while navigating complex compliance landscapes. Effective cybersecurity management goes beyond installing firewalls or antivirus software. It requires integrated governance, clear accountability, risk-informed decision making, and ongoing resilience building. For decision-makers in Australia, New Zealand, the United States, and Dubai, understanding how to structure and sustain a cybersecurity program has become essential to business continuity and stakeholder trust.
Understanding Cybersecurity Management Frameworks
Organizations require a structured foundation for cybersecurity management rather than ad-hoc responses to emerging threats. Frameworks provide that foundation by organizing security activities into logical categories, establishing common language, and connecting technical controls to business objectives.
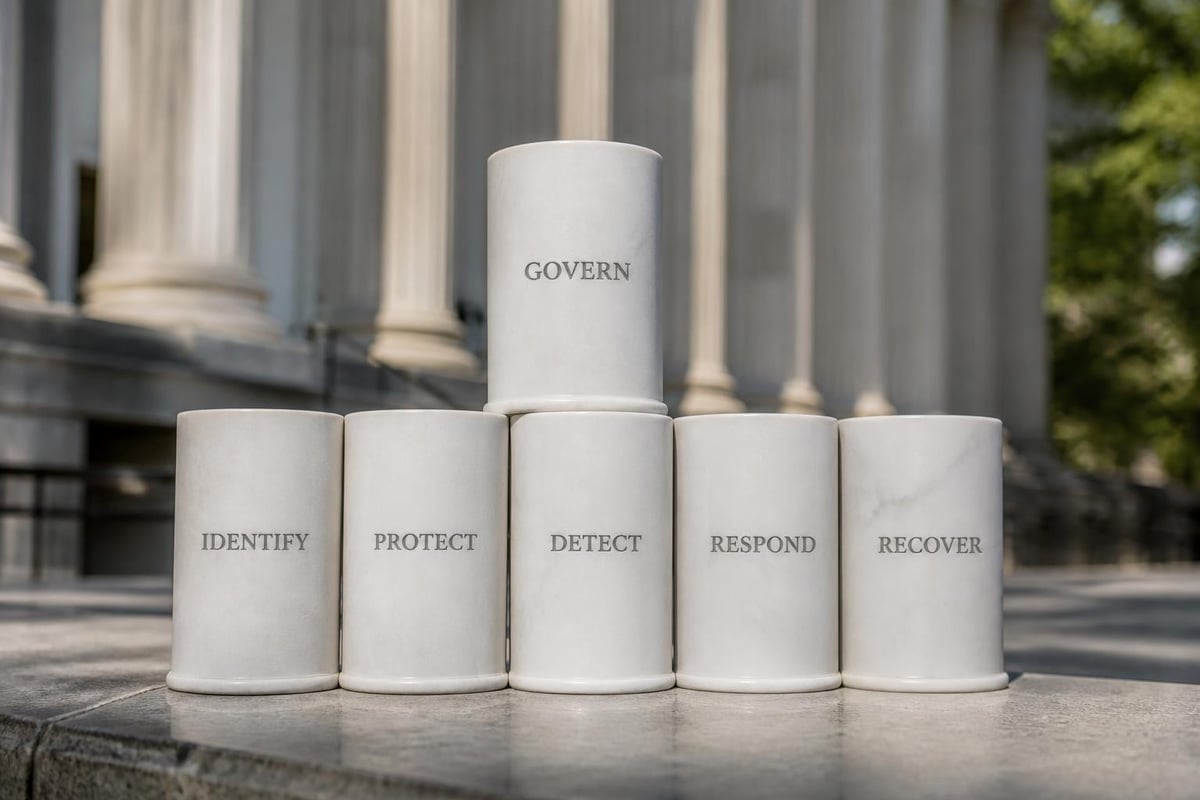
The NIST Cybersecurity Framework (CSF) 2.0 offers a widely adopted approach organized around six core functions: Govern, Identify, Protect, Detect, Respond, and Recover. The Govern function, introduced in version 2.0, explicitly addresses cybersecurity governance, risk management strategy, and organizational context. This elevation of governance reflects the reality that effective cybersecurity management begins with leadership commitment and strategic alignment.
Selecting the Right Framework for Your Organization
Different frameworks serve different purposes within cybersecurity management. ISO 27001 provides a certifiable information security management system structure, emphasizing documentation, risk assessment methodology, and continual improvement. The CIS Controls offer prescriptive, prioritized implementation guidance organized by enterprise size and security maturity.
Organizations often benefit from combining frameworks rather than selecting only one. A company might implement ISO 27001:2022 ISMS Implementation to establish systematic risk management and achieve certification, while referencing CIS Controls for specific technical implementation guidance. This hybrid approach leverages the certification value of ISO 27001 alongside the practical, threat-informed recommendations from CIS.
For organizations operating across multiple jurisdictions, understanding regional regulatory frameworks becomes part of cybersecurity management. European entities subject to NIS2 requirements can reference the ENISA NIS2 Technical Implementation Guidance for supply-chain security and cross-border incident reporting requirements.
Governance and Accountability Structures
Effective cybersecurity management requires clear governance structures that define who makes decisions, who implements controls, and who monitors outcomes. Without explicit accountability, security initiatives lose momentum and risk assessments become academic exercises disconnected from operational reality.
Key governance components include:
- Executive sponsorship and board oversight
- Defined roles and responsibilities across business units
- Documented policies, standards, and procedures
- Risk appetite statements that guide decision-making
- Regular management review cycles
Harvard Business Review's analysis highlights that boards often focus on technical details rather than strategic risk questions. Effective cybersecurity management shifts board conversations toward business impact, risk tolerance, and resource allocation decisions that enable security teams to function effectively.
Establishing Clear Roles and Responsibilities
Many organizations struggle with accountability because security responsibilities remain undefined or assumed rather than explicitly assigned. A comprehensive cybersecurity management program documents who owns specific security domains, who executes controls, and who verifies effectiveness.
| Role | Primary Accountability | Example Responsibilities |
|---|---|---|
| Board of Directors | Strategic oversight and risk appetite | Approve cybersecurity strategy, review major incidents, allocate resources |
| Executive Leadership | Program direction and resource allocation | Establish security priorities, fund initiatives, remove barriers |
| Security Team | Design, implementation, and monitoring | Assess risks, deploy controls, manage incidents, report metrics |
| Business Unit Owners | Domain-specific risk management | Implement controls in their areas, report issues, participate in exercises |
| All Employees | Adherence to policies and awareness | Follow security procedures, report suspicious activity, complete training |
Organizations can strengthen accountability by documenting these relationships through governance frameworks and GRC strategy that connect strategic objectives to operational activities. This documentation prevents the common scenario where everyone assumes security is someone else's responsibility.
Risk-Based Cybersecurity Management
Risk management forms the foundation of effective cybersecurity management. Organizations face unlimited potential threats but operate with finite resources, making risk-informed prioritization essential. A structured risk management process identifies what matters most, allocates resources accordingly, and provides measurable evidence of security investment value.
The risk management cycle includes:
- Asset identification - Cataloging information assets, systems, and data requiring protection
- Threat and vulnerability assessment - Understanding what could go wrong and existing weaknesses
- Impact and likelihood analysis - Evaluating potential business consequences and probability
- Risk evaluation - Comparing risks against appetite and tolerance thresholds
- Treatment decision - Selecting appropriate responses (mitigate, accept, transfer, avoid)
- Control implementation - Deploying selected safeguards
- Monitoring and review - Verifying control effectiveness and reassessing risk
Operationalizing Risk Assessments
Many organizations conduct annual risk assessments that produce lengthy reports but generate little security improvement. Effective cybersecurity management transforms risk assessment from compliance exercise to operational tool. This requires translating identified risks into actionable control requirements, assigning ownership, establishing implementation timelines, and tracking progress.
For businesses without dedicated security teams, partnering with specialists who provide information security risk management services delivers the expertise needed to conduct thorough assessments while building internal capability over time. This approach prevents the common pitfall of theoretical risk registers that never translate into improved security posture.
Organizations should also connect risk assessments to threat intelligence. The MITRE ATT&CK framework provides a knowledge base of adversary tactics and techniques observed in real-world attacks. By mapping identified risks to ATT&CK techniques, security teams can prioritize defenses against methods actually used by threat actors rather than theoretical vulnerabilities.
Control Implementation and Operational Security
Cybersecurity management extends beyond identifying risks to implementing and operating effective controls. Control implementation requires understanding the technical landscape, selecting appropriate solutions, integrating them into existing environments, and ensuring they function as intended.
Control categories within cybersecurity management include:
- Technical controls - Firewalls, encryption, access management, monitoring tools
- Administrative controls - Policies, procedures, training, governance processes
- Physical controls - Facility security, device management, media handling
Organizations frequently focus disproportionately on technical controls while neglecting administrative safeguards. Effective cybersecurity management maintains balance across control categories, recognizing that documented procedures and trained personnel often deliver greater risk reduction than additional security tools.
Building Security Operations Capability
Many mid-sized organizations face a critical question: Should we build internal security operations or partner with specialists? This decision directly impacts cybersecurity management sustainability and cost-effectiveness.
Building internal capability requires recruiting skilled personnel, investing in security tools, establishing processes, and maintaining 24/7 coverage. Organizations pursuing this path often discover that security talent shortages, tool complexity, and operational overhead exceed initial projections.
Partnering with providers offering managed SOC services delivers immediate access to trained analysts, established processes, and integrated security tools. This approach allows organizations to focus internal resources on business-aligned security activities like risk assessment and governance while specialists handle monitoring, threat detection, and initial incident response.
The partnership model particularly benefits organizations in Australia, New Zealand, Dubai, and regions where local security talent remains scarce or prohibitively expensive. Managed services provide scalability, allowing security capabilities to grow with business needs without long recruitment cycles or capital investment in security infrastructure.
Incident Response and Business Continuity
No cybersecurity management program prevents all incidents. Effective programs prepare for inevitable security events through documented response procedures, trained response teams, and regular testing. Organizations that plan incident response systematically recover faster, experience less business disruption, and reduce incident costs compared to those reacting without preparation.
The CISA Federal Government Cybersecurity Incident and Vulnerability Response Playbooks provide structured guidance for response planning, including detection thresholds, escalation procedures, communication protocols, and recovery steps. While designed for government entities, the playbook structure applies equally to commercial organizations.
Developing Effective Response Plans
Incident response plans should address:
- Detection and analysis - How incidents are identified, triaged, and scoped
- Containment - Immediate steps to limit damage and prevent spread
- Eradication - Removing threats and closing vulnerabilities
- Recovery - Restoring normal operations and verifying system integrity
- Lessons learned - Post-incident review and improvement identification
Many organizations create comprehensive incident response plans that fail during actual incidents because teams never practiced executing them. Cybersecurity management includes regular tabletop exercises that simulate scenarios like ransomware attacks, data breaches, or supply chain compromises. These exercises identify gaps, clarify responsibilities, and build response muscle memory before real incidents occur.
Continuous Monitoring and Improvement
Cybersecurity management represents an ongoing process rather than a one-time project. Threats evolve, business contexts change, new vulnerabilities emerge, and regulatory requirements expand. Organizations maintaining effective security posture embed continuous monitoring and improvement into their management systems.
Monitoring mechanisms include:
- Security metrics and key performance indicators
- Control effectiveness testing and validation
- Vulnerability scanning and assessment
- Threat intelligence review and integration
- Compliance audits and assessments
Measuring Cybersecurity Program Effectiveness
Effective measurement connects security activities to business outcomes rather than simply counting technical metrics. While numbers of blocked emails or detected vulnerabilities provide operational insight, executive stakeholders require metrics that demonstrate security program value in business terms.
| Metric Category | Technical Indicators | Business Indicators |
|---|---|---|
| Prevention | Vulnerabilities patched, controls deployed | Prevented incident cost, compliance violations avoided |
| Detection | Mean time to detect (MTTD), alert volume | Incidents detected before business impact, data loss prevented |
| Response | Mean time to respond (MTTR), containment speed | Business downtime avoided, customer impact minimized |
| Resilience | Recovery time objective (RTO) achievement | Revenue protected, reputation maintained |
Organizations can strengthen measurement programs by establishing baselines, tracking trends over time, and comparing performance against industry benchmarks. This longitudinal view demonstrates improvement, justifies security investments, and identifies areas requiring additional focus.
Supply Chain and Third-Party Risk
Modern businesses rely on complex ecosystems of suppliers, service providers, cloud platforms, and technology vendors. This interconnection expands the attack surface beyond organizational boundaries, making supply chain security a critical component of cybersecurity management.
Recent high-profile incidents demonstrate that attackers often target trusted suppliers as pathways to ultimate victims. Effective cybersecurity management extends risk assessment and control requirements to third parties based on the access, data, and criticality they represent.
Third-party risk management activities include:
- Due diligence - Assessing supplier security posture before engagement
- Contract requirements - Embedding security obligations in agreements
- Access controls - Limiting supplier privileges to legitimate needs
- Ongoing monitoring - Reviewing supplier security practices over time
- Incident coordination - Establishing procedures for supplier-related incidents
Organizations can formalize these activities through third-party supplier risk programs that categorize suppliers by risk level and apply proportionate security requirements. This prevents both under-control of critical suppliers and excessive burden on low-risk vendors.
Application Security and Secure Development
For organizations developing software, mobile applications, or web services, application security becomes integral to cybersecurity management. Development teams working under schedule pressure sometimes view security as impediment rather than enabler, creating tension that undermines both security and development velocity.
Effective application security integrates safeguards throughout the development lifecycle rather than treating security as a final pre-release gate. This "shift left" approach identifies and addresses vulnerabilities during design and coding when fixes cost less and cause less disruption.
The OWASP Top Ten identifies the most critical web application security risks, providing developers and security teams with focused guidance on common vulnerability categories. Organizations building applications should ensure development teams understand these risks and implement coding practices that prevent them.
Secure development lifecycle components include:
- Security requirements during design
- Secure coding standards and training
- Code review and static analysis
- Dynamic security testing before release
- Vulnerability disclosure and patch management after deployment
Organizations can further strengthen application security by implementing managed VAPT and forensics services that examine applications from an attacker's perspective, identifying weaknesses before adversaries exploit them. Regular penetration testing validates that theoretical security controls function effectively against real-world attack techniques.
Emerging Technologies and Artificial Intelligence
The rapid adoption of artificial intelligence and machine learning technologies introduces new considerations for cybersecurity management. Organizations deploying AI systems face unique risks including model poisoning, adversarial inputs, data privacy violations, and unintended algorithmic bias. Traditional security controls designed for deterministic systems may not adequately address AI-specific threats.
Effective cybersecurity management in 2026 addresses AI security through multiple dimensions:
- AI system security - Protecting AI models, training data, and inference engines from attack
- AI-powered security tools - Leveraging AI to enhance threat detection and response
- AI governance - Establishing oversight for AI development and deployment
- Privacy and ethics - Ensuring AI systems handle data appropriately and operate fairly
Organizations deploying AI should connect security requirements to application behavior and business context. Microsoft's Security Operations documentation provides practical guidance on integrating AI systems into security operations while maintaining appropriate oversight and monitoring.
Compliance and Regulatory Considerations
Cybersecurity management increasingly intersects with regulatory compliance as governments worldwide implement security and privacy requirements. Organizations operating across multiple jurisdictions face particularly complex compliance landscapes with overlapping and sometimes conflicting requirements.
Rather than treating compliance as separate from security, effective cybersecurity management integrates regulatory requirements into the overall risk and control framework. This approach prevents duplication, reduces compliance costs, and ensures security investments satisfy multiple objectives simultaneously.
Common regulatory frameworks affecting cybersecurity management include:
- Data protection - GDPR, Australian Privacy Act, California Consumer Privacy Act
- Industry-specific - HIPAA (healthcare), PCI DSS (payment cards), GLBA (financial services)
- National security - Essential Eight (Australia), NIS2 (European Union), CMMC (US defense)
- Cross-border - CLOUD Act, data localization requirements, transfer mechanisms
Organizations can streamline compliance by mapping requirements to control frameworks like ISO 27001, implementing controls once, and documenting how each control satisfies multiple regulatory obligations. This unified approach, documented through policies, standards, and procedures, reduces administrative overhead while strengthening overall security posture.
Building Security Awareness and Culture
Technology controls represent only part of effective cybersecurity management. Human behavior significantly influences security outcomes, making awareness and culture-building essential program components. Organizations with strong security cultures experience fewer incidents, detect threats faster, and recover more effectively because employees understand their role in security and act accordingly.
Security awareness programs should move beyond annual compliance training toward ongoing engagement that builds genuine understanding and behavior change. Effective programs include:
- Role-based training - Tailoring content to specific job functions and risks
- Simulated phishing - Testing awareness and providing immediate feedback
- Regular communications - Reinforcing messages through multiple channels
- Leadership modeling - Executives demonstrating security commitment
- Recognition programs - Acknowledging employees who support security
Organizations investing in comprehensive security awareness training programs see measurable improvements in metrics like phishing click rates, password hygiene, and incident reporting. These behavioral changes often deliver greater risk reduction than technical controls alone, particularly against social engineering attacks that bypass technology safeguards.
Choosing the Right Cybersecurity Management Partner
Organizations without internal security expertise face important decisions about building capability, hiring staff, or partnering with specialists. For many mid-sized businesses, the partnership model delivers the most effective and cost-efficient cybersecurity management solution.
When evaluating potential partners, consider:
- Relevant certifications - Professional qualifications demonstrating expertise
- Service scope - Whether offerings address your specific needs
- Response availability - How quickly the provider can engage when issues arise
- Geographic understanding - Familiarity with regional regulatory requirements
- Integration approach - How services connect to your existing operations
- Transparency - Clarity about what's included versus additional costs
Organizations should seek partners who take time to understand business context, risk tolerance, and operational constraints rather than proposing generic solutions. Effective cybersecurity management requires alignment between security measures and business objectives, which only occurs when providers invest in understanding your unique situation.
For businesses exploring F&C's comprehensive services, the managed approach provides access to experienced professionals, established methodologies, and proven tools without the overhead of building internal capability. This model allows organizations to focus resources on core business activities while maintaining robust security posture.
Cybersecurity management in 2026 requires structured approaches that connect governance, risk assessment, control implementation, and continuous improvement into cohesive programs. Organizations that invest in systematic security management protect themselves more effectively while demonstrating responsible stewardship to customers, partners, and regulators. Whether you're establishing your first formal security program or enhancing existing capabilities, F&C offers the expertise and partnership approach to build resilient, business-aligned cybersecurity management. Contact us to discuss how we can support your specific requirements and help you develop a security program that protects what matters most.