Security as a Service: A Guide for Business Leaders
Business leaders today face an expanding array of cybersecurity threats while simultaneously managing constrained budgets and talent shortages. Security as a service has emerged as a practical response to this challenge, enabling organizations to access enterprise-grade protection without building and maintaining complex internal security infrastructure. This delivery model shifts the burden of security operations, compliance monitoring, and threat intelligence to specialized external providers who deliver capabilities through cloud-based platforms and managed services.
What Security as a Service Means in Practice
Security as a service (SECaaS) represents a fundamental shift in how organizations acquire and operate cybersecurity capabilities. Rather than purchasing software licenses, deploying hardware appliances, and staffing internal security teams, businesses consume security functions as ongoing services delivered by external specialists.
The Cloud Security Alliance defines security as a service as a business and delivery model where security capabilities are provided through cloud-based or managed service offerings. This approach allows organizations to leverage specialized expertise, advanced tooling, and continuous monitoring without the capital expenditure and operational complexity of traditional security implementations.
Core Components of SECaaS Delivery
Security as a service encompasses multiple functional domains, each addressing specific protection requirements:
- Threat detection and response through managed security operations centers
- Vulnerability assessment and penetration testing delivered as recurring engagements
- Compliance monitoring and reporting aligned with regulatory frameworks
- Identity and access management provided through cloud platforms
- Data protection and encryption delivered as platform capabilities
- Security awareness training through online learning environments
The CISA Cloud Security Technical Reference Architecture provides authoritative guidance on how security as a service integrates with broader cloud architectures and shared responsibility models.
Organizations typically adopt security as a service incrementally, starting with high-priority capabilities such as email security or endpoint protection, then expanding coverage as they gain confidence in the delivery model.
Why Organizations Choose Security as a Service
The decision to adopt security as a service reflects both strategic priorities and practical constraints. Business leaders in Australia, New Zealand, the United States, and Dubai increasingly recognize that building internal security capabilities requires sustained investment in talent, technology, and processes that many organizations cannot economically justify.
Access to specialized expertise represents perhaps the most compelling driver. Cybersecurity professionals with deep technical knowledge and relevant certifications command premium salaries, and the global shortage of qualified practitioners makes recruitment exceptionally challenging. Security as a service providers maintain teams of specialists who develop expertise across multiple client environments and threat scenarios.
Predictable operational costs replace the variable expenses associated with internal security programs. Rather than budgeting for security staff turnover, technology refresh cycles, and unexpected incident response costs, organizations pay consistent monthly or annual fees that align with their consumption of security services.
| Traditional Security Model | Security as a Service |
|---|---|
| Capital expenditure for tools | Operational expenditure only |
| Recruit and retain specialists | Access provider expertise |
| Manage technology lifecycle | Provider handles updates |
| Variable incident costs | Predictable service fees |
| Limited to internal knowledge | Benefit from multi-client intelligence |
The business case for security as a service strengthens when organizations evaluate the total cost of achieving specific protection outcomes rather than simply comparing software licensing costs. Managed cybersecurity services provide comprehensive capabilities that would require multiple internal hires and technology investments to replicate.
Rapid Deployment and Scalability
Security as a service enables faster time-to-value compared to traditional implementations. Providers deliver preconfigured capabilities through established platforms, eliminating lengthy procurement, installation, and configuration cycles. Organizations facing regulatory deadlines or responding to specific threats can activate protection rapidly.
Scalability benefits emerge as organizations grow, enter new markets, or adjust their security posture. Adding coverage for new locations, applications, or user populations typically requires only subscription adjustments rather than infrastructure expansion.
Key Security as a Service Capabilities
Understanding the specific functions available through security as a service helps buyers evaluate which capabilities best address their requirements. The following domains represent the most commonly consumed SECaaS offerings in 2026.
Managed Detection and Response
Managed Detection and Response (MDR) services provide continuous monitoring of network traffic, endpoint activity, and application behavior to identify potential security incidents. The Cloud Security Alliance explains how MDR achieves cyber resilience by combining technology platforms with human expertise to detect, investigate, and respond to threats.
Organizations receive 24/7 security monitoring without maintaining internal security operations center (SOC) staffing. When the MDR provider detects suspicious activity, security analysts investigate the alert, determine its severity, and coordinate response actions with the client organization.
MDR services typically include:
- Collection and analysis of security telemetry from multiple sources
- Threat hunting to proactively identify indicators of compromise
- Incident triage and investigation by security analysts
- Coordinated response including containment and remediation guidance
- Post-incident reporting and lessons learned documentation
The effectiveness of MDR depends heavily on the quality of integration between the provider's platform and the client's environment. Organizations should expect to invest time in initial onboarding, ensuring that security sensors are properly deployed and that escalation procedures are clearly defined.
Vulnerability Assessment and Penetration Testing
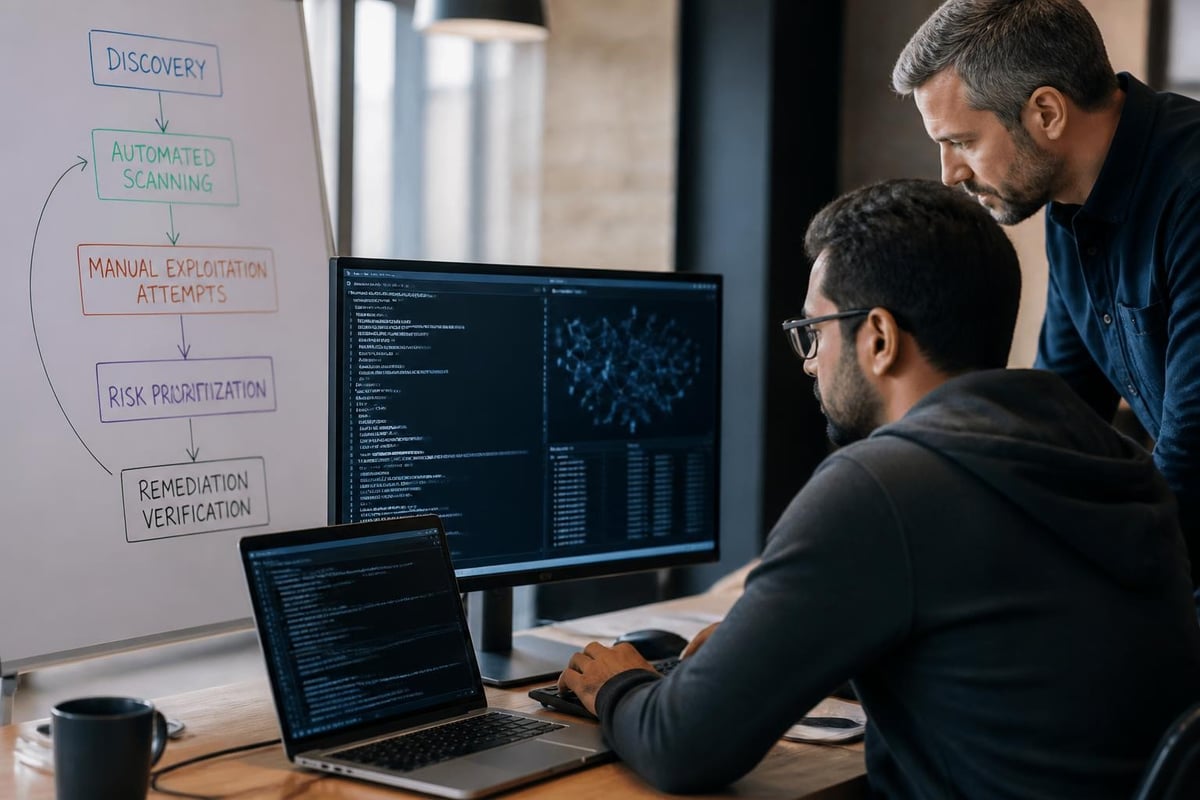
Regular security testing identifies weaknesses before attackers exploit them. Security as a service providers deliver vulnerability assessment and penetration testing as recurring engagements rather than one-time projects, ensuring that protection keeps pace with evolving threats and infrastructure changes.
Vulnerability assessments use automated scanning tools to identify known weaknesses in networks, applications, and systems. Penetration testing goes further, employing skilled security professionals who attempt to exploit identified vulnerabilities to demonstrate real-world risk.
Organizations benefit from the provider's investment in testing tools, methodologies, and ongoing training that keeps security testers current with emerging attack techniques.
Compliance Management and Reporting
Maintaining compliance with regulatory frameworks requires continuous evidence collection, control monitoring, and documentation. Security as a service providers deliver compliance monitoring and reporting capabilities that automate much of this burden.
These services align security controls with specific regulatory requirements such as ISO 27001, SOC 2, or industry-specific mandates. The provider's platform collects evidence of control operation, identifies gaps, and generates reports that demonstrate compliance status to auditors and regulators.
Organizations pursuing certification for frameworks like ISO 27001 benefit from providers who understand both the technical security controls and the governance processes required for successful certification. The relationship between information security management systems and ongoing security operations becomes more manageable when a single provider delivers both the framework implementation and the operational capabilities.
Evaluating Security as a Service Providers
Selecting the right security as a service provider requires careful evaluation of both technical capabilities and service delivery characteristics. Business leaders should approach this decision with the same rigor applied to any strategic vendor relationship.
Technical Competence and Certifications
Provider staff should hold relevant professional certifications that demonstrate competence in security operations, incident response, and the specific technologies deployed in your environment. Ask providers to explain which certifications their security analysts maintain and how they ensure staff remain current.
The provider's own security posture matters significantly. Organizations entrust SECaaS providers with access to sensitive systems and data, making the provider's internal security practices a critical evaluation criterion. Review the provider's own compliance certifications and ask about their approach to protecting client data.
Service Level Agreements and Response Expectations
Clarity around service levels prevents misunderstandings and establishes accountability. Security as a service agreements should specify:
- Detection timeframes for different threat categories
- Initial response times for security incidents
- Escalation procedures and contact paths
- Availability commitments for monitoring platforms
- Reporting frequency and formats for compliance and operational metrics
Organizations should understand that security as a service providers typically offer responsive support rather than guaranteed response times. The distinction matters when evaluating provider capabilities and setting internal expectations.
| Evaluation Criteria | Questions to Ask |
|---|---|
| Technical capabilities | What tools and platforms do you use for detection and response? |
| Staff expertise | What certifications do your security analysts hold? |
| Client integration | How do you integrate with our existing security tools? |
| Incident handling | Walk me through a recent incident response scenario |
| Compliance experience | Have you worked with organizations in our industry? |
| Contract flexibility | Can we adjust scope as our requirements change? |
Geographic and Regulatory Considerations
Organizations operating in multiple jurisdictions should verify that providers understand regional regulatory requirements. Security as a service providers serving clients in Australia, New Zealand, the United States, and Dubai must navigate different data sovereignty, privacy, and industry-specific regulations.
Ask providers how they handle data residency requirements and whether their service delivery model accommodates jurisdiction-specific compliance obligations. The NIST guidance on cloud access control provides a framework for understanding how responsibility divides between service providers and consumers.
Integration with Existing Security Infrastructure
Security as a service rarely operates in isolation. Most organizations maintain some internal security capabilities, whether basic endpoint protection, network firewalls, or identity management systems. Successful SECaaS adoption requires thoughtful integration between external services and existing infrastructure.
Data Flow and Tool Integration
The provider's monitoring and detection capabilities depend on receiving relevant security telemetry from across your environment. This requires integration between your existing security tools and the provider's platform. Common integration points include:
- Security information and event management (SIEM) platforms that aggregate logs
- Endpoint detection and response (EDR) agents deployed on workstations and servers
- Network traffic analysis tools that inspect communications
- Cloud security posture management platforms monitoring infrastructure-as-a-service configurations
- Identity providers that supply authentication and authorization data
Organizations should budget time and resources for initial integration work. While security as a service reduces long-term operational burden, successful deployment requires upfront investment in connecting systems and validating data flow.
Preserving Internal Security Governance
Adopting security as a service does not eliminate the organization's responsibility for security governance and risk management. Leadership must maintain clear accountability for security outcomes even when operational execution shifts to external providers.
The governance and compliance framework should explicitly address how security as a service integrates with internal risk management processes, who holds decision authority for different security actions, and how the organization maintains visibility into security posture.
Common Implementation Challenges
Organizations adopting security as a service encounter predictable challenges during implementation and early operation. Understanding these obstacles allows buyers to anticipate requirements and plan accordingly.
Skills transfer expectations often create friction. Organizations sometimes expect that security as a service will instantly provide comprehensive protection without any internal involvement. In reality, the provider requires ongoing collaboration with internal teams who understand business context, application architecture, and acceptable risk tradeoffs.
Alert fatigue emerges when detection systems generate more notifications than the organization can effectively process. Security as a service providers tune detection rules based on observed activity in your environment, but this optimization takes time and requires feedback about false positives and business-acceptable behaviors.
Incident response coordination requires clear procedures. When the provider identifies a security incident, internal teams must understand their role in containment, investigation, and recovery. Organizations should document and test these procedures before experiencing an actual incident.
The SANS Institute's research on managed detection and response offers practical guidance on optimizing the relationship between organizations and their security service providers.
Strategic Considerations for 2026 and Beyond
The security as a service market continues evolving as threats become more sophisticated and organizations face increasing regulatory pressure. Several trends shape how forward-thinking organizations approach SECaaS in 2026.
Artificial Intelligence in Security Operations
Security providers increasingly incorporate artificial intelligence and machine learning into detection, investigation, and response workflows. These capabilities analyze larger volumes of security data, identify subtle patterns indicating compromise, and reduce the time required to investigate alerts. Organizations evaluating security as a service should understand how providers deploy AI capabilities and what safeguards protect against algorithmic errors or biases.
The Trend Micro 2025 Cloud Security Report highlights how automation and AI-driven security analysis shape contemporary threat detection and response.
Consolidation and Platform Approaches
Organizations increasingly prefer providers who deliver multiple security capabilities through integrated platforms rather than managing relationships with numerous point-solution vendors. This consolidation reduces integration complexity and provides more coherent visibility across security domains.
When evaluating security as a service, consider whether the provider can expand scope to address additional requirements as your program matures. Providers offering managed security operations, vulnerability testing, and compliance management through coordinated delivery create efficiencies that single-capability providers cannot match.
Regulatory Compliance as a Driver
Regulatory requirements continue expanding globally, with frameworks addressing data privacy, critical infrastructure protection, and emerging technologies. Organizations view security as a service as a means to maintain compliance without building internal expertise for every new regulation.
The academic literature, including recent research on cybersecurity as a service, examines how outsourced security models help small and medium enterprises address compliance obligations that would otherwise require prohibitive internal investment.
Making the Decision
Business leaders evaluating security as a service should frame the decision around outcomes rather than simply comparing costs to internal alternatives. The fundamental question is not whether security as a service costs more or less than internal capabilities, but whether it delivers superior protection, compliance assurance, and risk reduction relative to your organization's specific requirements.
Start by documenting your current security posture, identifying gaps, and clarifying what you need from security capabilities. This assessment should address:
- What threats represent the highest risk to your organization?
- What regulatory obligations must you maintain?
- What internal resources are available to support security operations?
- How quickly must you deploy enhanced capabilities?
- What budget constraints influence your options?
Compare multiple providers against these criteria, requesting specific examples of how they have addressed similar requirements for organizations in comparable situations. Review case studies that demonstrate relevant experience and ask for references from current clients.
Organizations in different regions may encounter varying levels of provider availability and capability. Research which providers serve your geographic markets and understand local regulatory requirements.
The decision to adopt security as a service should align with broader technology strategy. Organizations already embracing cloud-based business applications and infrastructure-as-a-service platforms typically find security as a service more natural than those maintaining predominantly on-premises environments.
Security as a service provides business leaders with a practical path to enterprise-grade protection without the complexity and cost of building internal security operations. Success requires careful provider evaluation, thoughtful integration with existing capabilities, and sustained collaboration between external specialists and internal teams. F&C delivers managed cybersecurity and compliance services tailored to organizations that need comprehensive protection without maintaining extensive internal security teams. Our approach combines technical expertise with deep understanding of regulatory requirements across multiple jurisdictions, providing the foundation for long-term security resilience. Contact us to discuss how our security capabilities align with your specific requirements.